


The best CompTIA CAS-005 exam simulator engine for you
To prepare to the CompTIA SecurityX Certification Exam test, we have different CAS-005 test dump versions to satisfy examinees' exam need. The CAS-005 practice test dumps of common PDF version are very convenient to use. You just download the files to your computer, your phone, ipad and any electronic devices to read. It just likes a CAS-005 study guide book. If you are used to reading paper book, suggest you print the electronic PDF file out.

When the CAS-005 practice test has a lot CompTIA SecurityX Certification Exam exam actual questions and answers, it's better to use exam simulator to prepare. It's a little hard for many people to understand and member so many questions in a short time. Using the CAS-005 exam simulator engine, you will get more effective and quicker interactive learning in the process. And the CompTIA CAS-005 exam simulator engine including PC test engine and online test engine will give you a pass mark % at the end of the test. The dumps content of two CAS-005 test engine versions are all the same, the only difference that the pc test engine only supports windows operating system, the CompTIA SecurityX Certification Exam exam simulator of online test engine supports windows/Mac/Android/IOS operating systems.
Strong guarantee to pass CompTIA CAS-005 test-100% pass rate and refund policy
We've set strong guarantee to promise you to pass CAS-005 test. Before you decide you buy it, there are the free demos for you to see part of the CAS-005 test questions and answers. All the dumps are finished by our IT master team with very high quality. After the market test, they are all almost 100% passing rate to pass CAS-005 tests.
Even if you don't pass the CAS-005 exam with our CompTIA dumps, no worry about it, we will give your all refund to balance the failure risk. More guarantee is, there is all 365-days free update for you if buy the CAS-005 test dumps from us. Once there is any test update, we will send to your email address at the first time. Choosing us, guarantee you to pass your CAS-005 exam with full great service!
CompTIA CAS-005 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Secure and convenient CAS-005 test online shopping experience
When you pay attention to our CAS-005 test dumps, you can try out the free demo first. After the check of free demos, if you think ok, just add it to the shopping cart. The process of buying CAS-005 test online in Test4Engine is very convenient, simple and secure. You needn't register account in our site, just add your product to the cart and confirm your receiving email and pay for it. After your payment, your email will receive our CAS-005 test questions in a few seconds to minutes. It's very fast to get the dumps. And in the mails, you can see the auto-generated account for you for the next use. The all payments are protected by the biggest international payment Credit Card system.
CompTIA SecurityX Certification Sample Questions:
A security engineer must implement controls to limit access between developer endpoints and a cloud provider bucket for data storage. Developers routinely save sensitive files to the bucket as part of their projects. The security engineer must reduce the risk of unintended data exposure.
Which of the following is the most appropriate control to implement?
- A. Deploy an ACL on the virtual private cloud to avoid public access.
- B. Implement context-aware reauthentication to the local system.
- C. Restrict HTTP POST and PUT traffic to specific URLs at the proxy.
- D. Require server-side encryption using a KMS in the cloud provider.
Correct Answer: A 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
Source code snippets for two separate malware samples are shown below: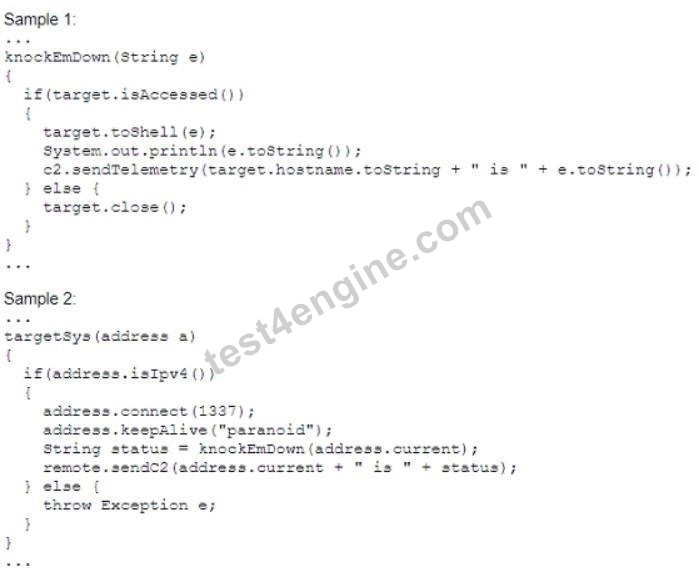
Which of the following describes the most important observation about the two samples?
- A. Both samples use IP connectivity for command and control.
- B. The samples were probably written by the same developer.
- C. Sample 1 is the target agent while Sample 2 is the C2 server.
- D. Telemetry is first buffered and then transmitted in paranoid mode.
Correct Answer: B 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
A customer requires secure communication of subscribed web services at all times, but the company currently signs its own certificate requests to an internal CA.
Which of the following approaches will best meet the customer's requirements?
- A. Submit a CSR for a wildcard certificate to a public CA.
- B. Generate a CSR to the local CA for email encryption.
- C. Process a CSR for a server authentication certificate.
- D. Request a software signing certificate from a public CA.
Correct Answer: C 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
A security engineer is developing a solution to meet the following requirements:
- All endpoints should be able to establish telemetry with a SIEM.
- All endpoints should be able to be integrated into the XDR platform.
- SOC services should be able to monitor the XDR platform
Which of the following should the security engineer implement to meet the requirements?
- A. WAF and syslog
- B. HIDS and vTPM
- C. HIPS and host-based firewall
- D. CDR and central logging
Correct Answer: C 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
A security configure is building a solution to disable weak CBC configuration for remote access connections lo Linux systems. Which of the following should the security engineer modify?
- A. The /etc/nsswitch.conf file, updating the name server
- B. The /etc/hostsfile, updating the IP parameter
- C. The /etc/sshd/ssh_configfile, updating the ciphers
- D. The /etc/openssl.conffile, updating the virtual site parameter
Correct Answer: C 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
Viewing page 1 out of 121 pages.
Viewing questions 1-5 out of 604 questions.


