


You choose to apply for Huawei Huawei Specialist because you know the society is full of competition and challenges. If you do not want HCIE-Security (Huawei Certified Internetwork Expert-Security) exam to become your stumbling block, you should consider our HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine or H12-731-ENU VCE test engine. Our Test4Engine is the leading position in this line and offer high-quality software test engine which can help you go through your examination. If you have no confidence for the Huawei HCIE-Security (Huawei Certified Internetwork Expert-Security) exam, our HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine will be your best select.

We have three versions for each exam dumps that: PDF dumps, Soft test engine, and APP on-line test engine. Totally the APP on-line test for engine is the most popular. Most candidates think about H12-731-ENU test for engine or HCIE-Security (Huawei Certified Internetwork Expert-Security) VCE test engine, they will choose APP on-line test engine in the end. The APP on-line test engine has many functions below.
1. HCIE-Security (Huawei Certified Internetwork Expert-Security) APP on-line test engine includes the exam practice questions and answers. You can practice whenever you want. H12-731-ENU VCE test engine includes 80% or so questions & answers of the real test. It is the foundation for passing exam. Of course, the PDF dumps & Soft test engine also have this function. (HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine)
2. HCIE-Security (Huawei Certified Internetwork Expert-Security) APP on-line test engine can imitate the real test; it can set timed test, mark your performance and point out your mistakes. (H12-731-ENU test for engine) It is really like the real test. It is helpful for clearing up your nervousness before test. The soft test engine also has this function but the PDF dumps do not.(HCIE-Security (Huawei Certified Internetwork Expert-Security) VCE test engine)
3. HCIE-Security (Huawei Certified Internetwork Expert-Security) APP on-line test engine can be installed in all operate systems. You can download HCIE-Security (Huawei Certified Internetwork Expert-Security) VCE test engine in your computers, iPhones, iWatch, MP4 or MP5 and so on. You can learn any time and any place you like. The soft test engine can just be installed in personal computers.
4. Statistically speaking, HCIE-Security (Huawei Certified Internetwork Expert-Security) APP on-line test engine is also stable than the soft test engine. It is more powerful.
Besides, you may doubt about our service. Yes, we guarantee your money and information safety. We make sure that "No Pass, No Pay". Our HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine can assist you go through the examination surely, meanwhile, our service will 100% satisfy you.
1. Our working time is 7*24, we will serve for you any time even on official holiday. You email or news about H12-731-ENU test for engine will be replied in 2 hours. Your questions & problems will be solved in 2 hours. After payment, you will receive our HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine & HCIE-Security (Huawei Certified Internetwork Expert-Security) VCE test engine soon.
2. We have professional IT staff who updates exam simulator engine every day so that all H12-731-ENU test for engine we sell out is latest & valid. Also we have a strict information system which can guarantee your information safety.
3. We support Credit Card payment so that your account and money will be safe certainly, you are totally worry-free shopping. We guarantee our HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine will assist you go through the examination surely. If you fail the exam unluckily we will refund you all the money you paid us unconditionally in one week. You get what you pay for.
More details please feel free to contact with us, we are pleased to serve for you. Give me a chance, I send you a success. HCIE-Security (Huawei Certified Internetwork Expert-Security) test for engine & H12-731-ENU VCE test engine will indeed be the best helper for your Huawei H12-731-ENU exam. If you choose us, you will 100% pass the exam for sure.
Huawei H12-731-ENU Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Cloud & Data Security | 12% | - Virtual firewall and cloud security solutions - Data security, encryption, and leakage prevention |
| Topic 2: Security O&M & Incident Response | 8% | - Incident response procedures and emergency handling - Security log analysis and monitoring |
| Topic 3: Threat Defense & Intrusion Prevention | 20% | - DDoS defense, single-packet attack protection - Vulnerability management and threat intelligence - IPS/IDS deployment and signature management |
| Topic 4: Security Architecture & Standards | 20% | - Information security standards and frameworks - Risk management and compliance requirements - Enterprise security architecture design principles |
| Topic 5: Firewall & Traffic Security Technologies | 25% | - Advanced firewall features and high availability - Virtual systems and multi-tenant security - NAT, bandwidth management, and security policies |
| Topic 6: VPN & Encryption Technologies | 15% | - PKI, certificate management, and encryption algorithms - VPN high reliability and troubleshooting - IPsec VPN, SSL VPN, and GRE over IPsec |
Huawei HCIE-Security (Huawei Certified Internetwork Expert-Security) Sample Questions:
IPsec tunnel communication is used between the headquarters and branch offices, in order to ensure the security of data transmission on the Internet. The administrator uses the dual-system hot backup function to improve the reliability of the communication between the headquarters and the branch offices, so as to avoid the failure of one USG in the headquarters and the failure of the branch offices to access the headquarters.
According to the following network diagram, which of the following statements is correct?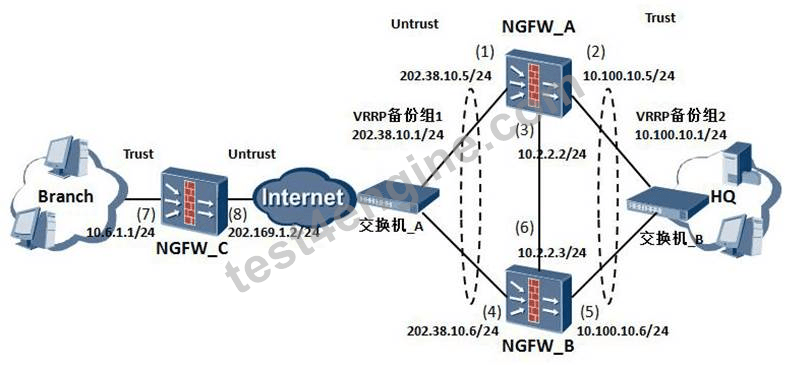
- A. Only IPsec dual-system hot backup in active/standby backup mode can be used.
- B. USG A , USG_B and USG_C only need to configure the route of the Internet, and there is no need to configure the route between the branch intranet and the headquarters intranet in USG_A , USG_B and USG_C.
- C. USG A , USG_B must enable NAT traversal.
- D. Only ESP and Tunnel mode encapsulation can be used.
Correct Answer: A,D 🗳️
According to the following networking, a customer uses the BGP traffic diversion policy route back injection method. Which of the following configurations must be configured on the cleaning device?
- A. firewall ddos bgp-next-hop fib-filter
- B. ip route-static 0.0.0.0 0 10.1.3.1
- C. interface GigabitEthernet2/0/2 anti-ddos flow-statistic enable
- D. firewall ddos bgp-next-hop 10.1.3.1
Correct Answer: D 🗳️
The terminal uses Agent for 802.1x authentication, the IP address of SC and Radius server is 172.18.10.68, and it always prompts network communication failure during authentication;
Viewing the Radius authentication log shows that the Radius authentication is successful and the authorization is ACL3001. The switch configuration is as follows:
dot1x enable
dot1x authentication-method eap
radius-server template lzy
radius-server shared-key simple 123456
radius-server authentication 172.18.10.68 1812
radius-server accounting1 72.1 3.10.63 1813
radius-server authorization 172.18.10.68 shared-key simple 123456
aaa
authentication-scheme default
authentication-scheme auth
authentication-mode radius
accounting-scheme acco
accounting-mode radius
accounting realtime 3
domain default
authentication-scheme auth
accounting-scheme acco
radius-server lzy
interface GigabitEthernet0/0/14
description connect 222
port hybrid pvid vlan 105
port hybrid untagged vlan 105
dot1x enable
acl number 3001
rule 1 permit ip destination 172.18.100.235 0
rule 2 permit ip destination 172.18.100.237 0
rule 10 deny ip
What could be the reason for the failure of network communication?
- A. AAA configuration error
- B. Billing configuration may be wrong
- C. GigabitEthernet0/0/14 port configuration error
- D. Authorization rule ACL configuration error
Correct Answer: D 🗳️
After the USG enables the HRP backup function, key configuration commands and session table status information will be synchronously backed up to the standby device in real time. What configuration commands and status information can be backed up?
- A. interface configuration command
- B. session table
- C. Attack Defense Command
- D. Virtual Firewall Command
- E. Forwarding Policy Commands
Correct Answer: B,C,E 🗳️
Using the SSL function of the USG gateway, the administrator can quickly and securely access all resources in the enterprise intranet, not only Web resources, and ensure that the communication between the client and the virtual gateway adopts the SSL security protocol, and the SSL client must ensure that the Without affecting access to other network resources, you can directly access Internet resources.
- A. Network extension in manual mode
- B. Network expansion in full routing mode
- C. port forwarding
- D. Network extension in split mode
Correct Answer: A 🗳️


