


[Dec 31, 2021] Get New SC-400 Certification Practice Test Questions Exam Dumps
Real SC-400 Exam Dumps Questions Valid SC-400 Dumps PDF
Exam SC-400: Microsoft Information Protection Administrator
The Information Protection Administrator plans and implements controls that meet organizational compliance needs. This person is responsible for translating requirements and compliance controls into technical implementation. They assist organizational control owners to become and stay compliant.
They work with information technology (IT) personnel, business application owners, human resources, and legal stakeholders to implement technology that supports policies and controls necessary to sufficiently address regulatory requirements for their organization. They also work with the compliance and security leadership such as a Chief Compliance Officer and Security Officer to evaluate the full breadth of associated enterprise risk and partner to develop those policies.
This person defines applicable requirements and tests IT processes and operations against those policies and controls. They are responsible for creating policies and rules for content classification, data loss prevention, governance, and protection.
Part of the requirements for: Microsoft Certified: Information Protection Administrator Associate
How to Register For Exam SC-400: Microsoft Information Protection Administrator?
NEW QUESTION 33
You plan to implement sensitivity labels for Microsoft Teams.
You need to ensure that you can view and apply sensitivity labels to new Microsoft Teams sites.
What should you do first?
- A. Create a new sensitivity label scoped to Groups & sites.
- B. Configure the EnableMTPLabels Azure Active Directory (Azure AD) setting.
- C. Run the Set-sposite cmdlet.
- D. Run the Execute-AzureAdLabelSync cmdtet.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-teams-groups-sites?view=o365-wo
NEW QUESTION 34
You are planning a data loss prevention (DLP) solution that will apply to computers that run Windows 10.
You need to ensure that when users attempt to copy a file that contains sensitive information to a USB storage device, the following requirements are met:
* If the users are members of a group named Group1, the users must be allowed to copy the file, and an event must be recorded in the audit log.
* All other users must be blocked from copying the file.
What should you create?
- A. one DLP policy that contains one DLP rule
- B. two DLP policies that each contains one DLP rule
- C. one DLP policy that contains two DLP rules
Answer: B
NEW QUESTION 35
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender fur Endpoint.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION 36
You have a Microsoft 365 subscription that uses Microsoft Exchange Online.
You need to receive an alert if a user emails sensitive documents to specific external domains.
What should you create?
- A. a data loss prevention (DLP) policy that uses the Privacy category
- B. a Microsoft Cloud App Security file policy
- C. a data loss prevention (DLP) alert filter
- D. a Microsoft Cloud App Security activity policy
Answer: A,D
NEW QUESTION 37
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You recently discovered that the developers at your company emailed Azure Storage keys in plain text to third parties.
You need to ensure that when Azure Storage keys are emailed, the emails are encrypted.
Solution: You configure a mail flow rule that matches a sensitive info type.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION 38
Each product group at your company must show a distinct product logo in encrypted emails instead of the standard Microsoft Office 365 logo.
What should you do to create the branding templates?
- A. Create a Transport rule.
- B. Run the New-OMEConfiguration cmdlet.
- C. Create an RMS template.
- D. Run the Set-IRMConfiguration cmdlet.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/add-your-organization-brand-to-encryptedmessages?
NEW QUESTION 39
You need to create a retention policy to retain all the files from Microsoft Teams channel conversations and private chats.
Which two locations should you select in the retention policy? Each correct answer present part of the solution.
NOTE: Each correct selection is worth one point.
- A. SharePoint sites
- B. Office 365 groups
- C. OneDrive accounts
- D. Exchange email
- E. Team channel messages
- F. Team chats
Answer: A,B
NEW QUESTION 40
You need to automatically apply a sensitivity label to documents that contain information about your company's network including computer names, IP addresses, and configuration information.
Which two objects should you use? Each correct answer presents part of the solution. (Choose two.) NOTE: Each correct selection is worth one point.
- A. a data loss prevention (DLP) policy
- B. a sensitive info type that uses keywords
- C. a custom trainable classifier
- D. a sensitivity label that has auto-labeling
- E. a sensitive info type that uses a regular expression
- F. an Information protection auto-labeling policy
Answer: C,F
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/classifier-learn-about?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365- worldwide
NEW QUESTION 41
Your company has a Microsoft 365 tenant that uses a domain named contoso.
The company uses Microsoft Office 365 Message Encryption (OMI ) to encrypt email sent to users in fabrikam.com.
A user named User1 erroneously sends an email to user2@fabrikam
You need to disable [email protected] from accessing the email.
What should you do?
- A. Run the Set-OMEMessageRevocation Cmdlet.
- B. Instruct User1 to delete the email from her Sent Items folder from Microsoft Outlook.
- C. Run the Get-MessageTrace Cmdlet.
- D. Run the New-ComplianceSearchAction cmdlet.
- E. instruct User1 to select Remove external access from Microsoft Outlook on the web.
Answer: C
NEW QUESTION 42
A user reports that she can no longer access a Microsoft Excel file named Northwind Customer Data.xlsx.
From the Cloud App Security portal, you discover the alert shown in the exhibit.
You restore the file from quarantine.
You need to prevent files that match the policy from being quarantined. Files that match the policy must generate an alert.
What should you do?
- A. Update the governance action.
- B. Exclude file matching by using a regular expression.
- C. Modify the policy template.
- D. Assign the Global reader role to the file owners.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/data-protection-policies#create-a-new-file-policy
NEW QUESTION 43
You have a data loss prevention (DLP) policy that applies to the Devices location. The policy protects documents that contain States passport numbers.
Users reports that they cannot upload documents to a travel management website because of the policy.
You need to ensure that the users can upload the documents to the travel management website. The solution must prevent the protected content from being uploaded to other locations.
Which Microsoft 365 Endpoint data loss prevention (Endpoint DLP) setting should you configure?
- A. Unallowed apps
- B. Service domains
- C. File path exclusions
- D. Unallowed browsers
Answer: A
NEW QUESTION 44
You have a Microsoft 365 tenant that uses Microsoft Teams.
You create a data loss prevention (DLP) policy to prevent Microsoft Teams users from sharing sensitive information.
You need to identify which locations must be selected to meet the following requirements:
* Documents that contain sensitive information must not be shared inappropriately in Microsoft Teams.
* If a user attempts to share sensitive information during a Microsoft Teams chat session, the message must be deleted immediately.
Which three locations should you select? To answer, select the appropriate locations in the answer area.
(Choose three.)
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Graphical user interface, application Description automatically generated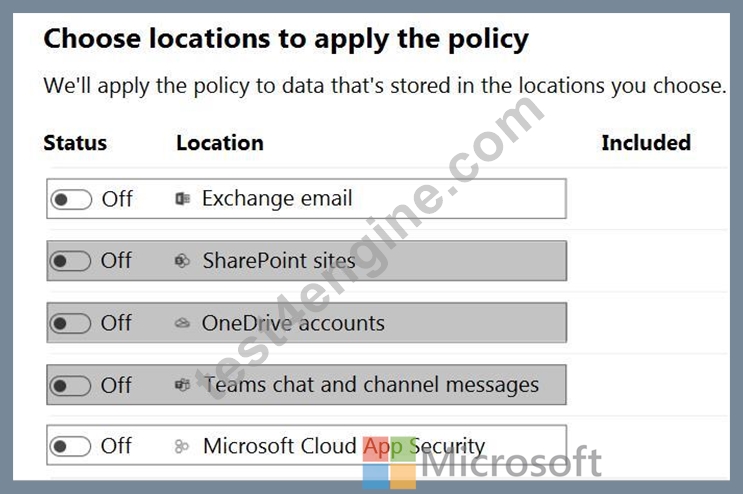
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-microsoft-teams?view=o365-worldwide
NEW QUESTION 45
You have a Microsoft 365 E5 tenant.
You create sensitivity labels as shown in the Sensitivity Labels exhibit.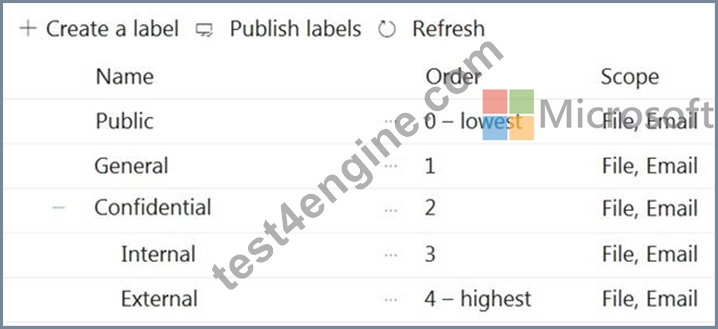
The Confidential/External sensitivity label is configured to encrypt files and emails when applied to content.
The sensitivity labels are published as shown in the Published exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.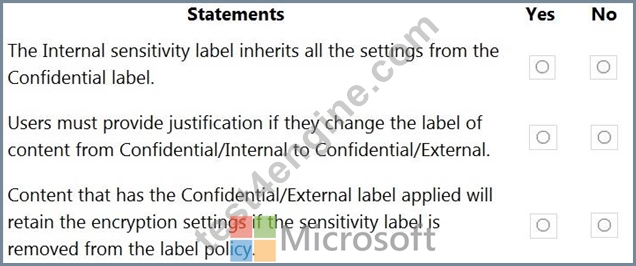
Answer:
Explanation: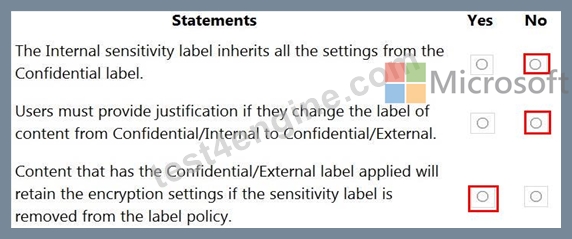
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION 46
You have a Microsoft 365 tenant named contoso.com that contains two users named User1 and User2. The tenant uses Microsoft Office 365 Message Encryption (OME).
User1 plans to send emails that contain attachments as shown in the following table.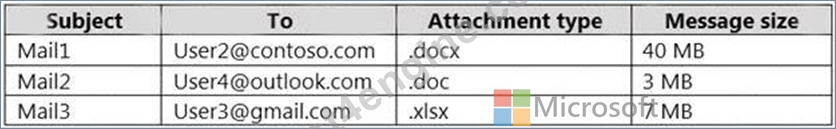
User2 plans to send emails that contain attachments as shown in the following table.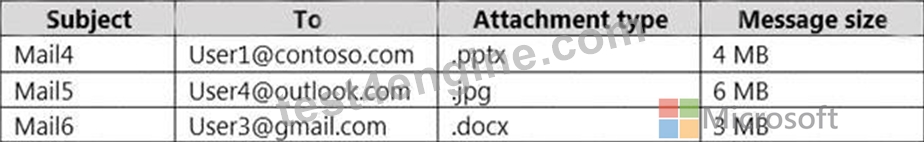
For which emails will the attachments be protected? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.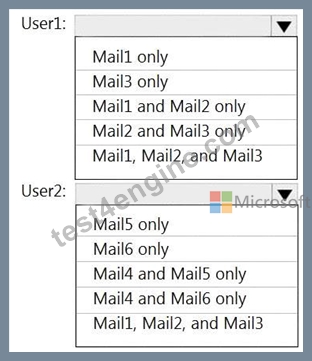
Answer:
Explanation: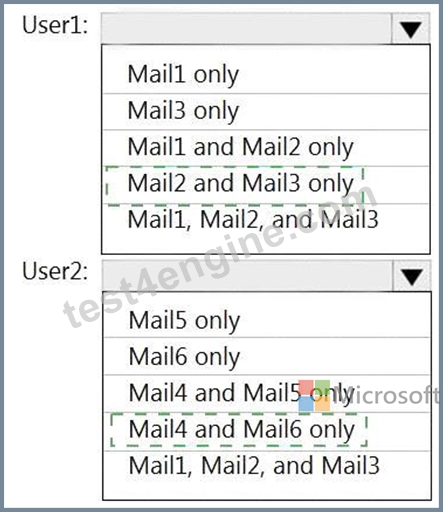
Explanation
Reference:
https://support.microsoft.com/en-gb/office/introduction-to-irm-for-email-messages-bb643d33-4a3f-4ac7-9770-fd
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome?view=o365-worldwide
https://docs.microsoft.com/en-us/office365/servicedescriptions/exchange-online-service-description/exchange-on
NEW QUESTION 47
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution:: You deploy the unified labeling client to the computers.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION 48
You have a Microsoft 365 tenant.
A retention hold is applied to all the mailboxes in Microsoft Exchange Online.
A user named User1 leaves your company, and the account of User1 is deleted from Azure Active Directory (Azure AD).
You need to create a new user named User2 and provide User2 with access to the mailbox of User1.
How should you complete the PowerShell command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.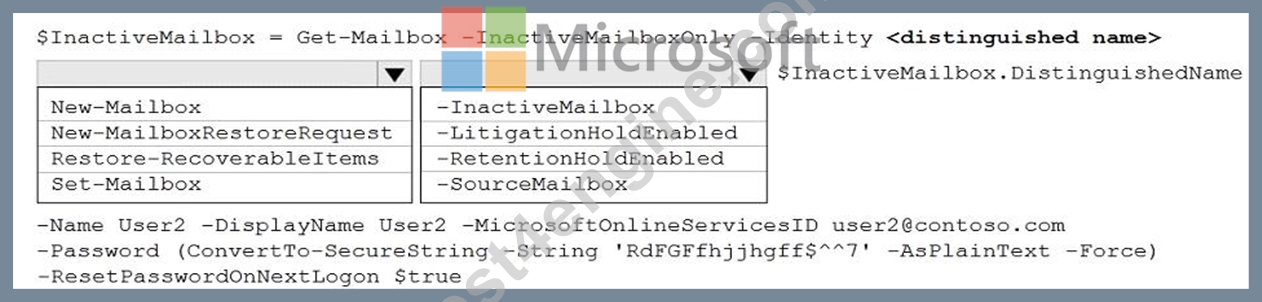
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/recover-an-inactive-mailbox?view=o365-worldwide
NEW QUESTION 49
You need to meet the technical requirements for the creation of the sensitivity labels.
To which user or users must you grant the Sensitivity label administrator role?
- A. Admin1, Admin2, Admin4, and Admin5 only
- B. Admin1 only
- C. Admin1, Admin2, and Admin3 only
- D. Admin1 and Admin5 only
- E. Admin1 and Admin4 only
Answer: E
Explanation:
Explanation
Compliance Data Administrator, Compliance Administrator, and Security Administrator already have the required permissions to create the labels.
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/get-started-with-sensitivity-labels?view=o365- worldwide#permissions-required-to-create-and-manage-sensitivity-labels
NEW QUESTION 50
While creating a retention label, you discover that the following options are missing:
* Mark items as a record
* Mark items are a regular record
You need to ensure that the options are available when you create label in the Microsoft 365 compliance center.
How should you complete the PowerShell script? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.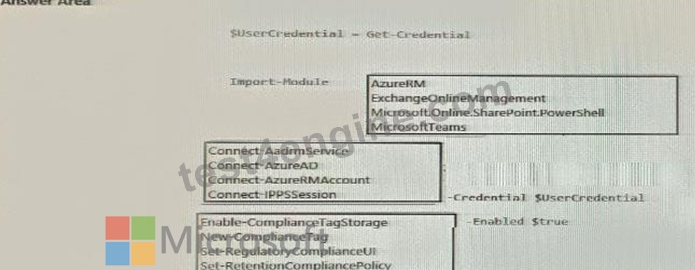
Answer:
Explanation: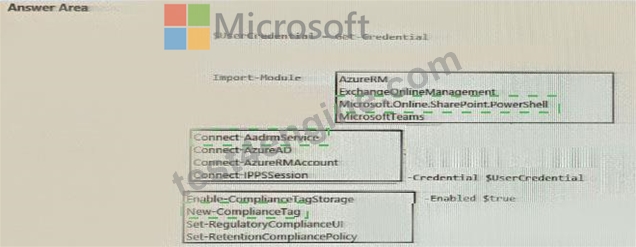
NEW QUESTION 51
You are configuring a retention label named Label1 as shown in the following exhibit.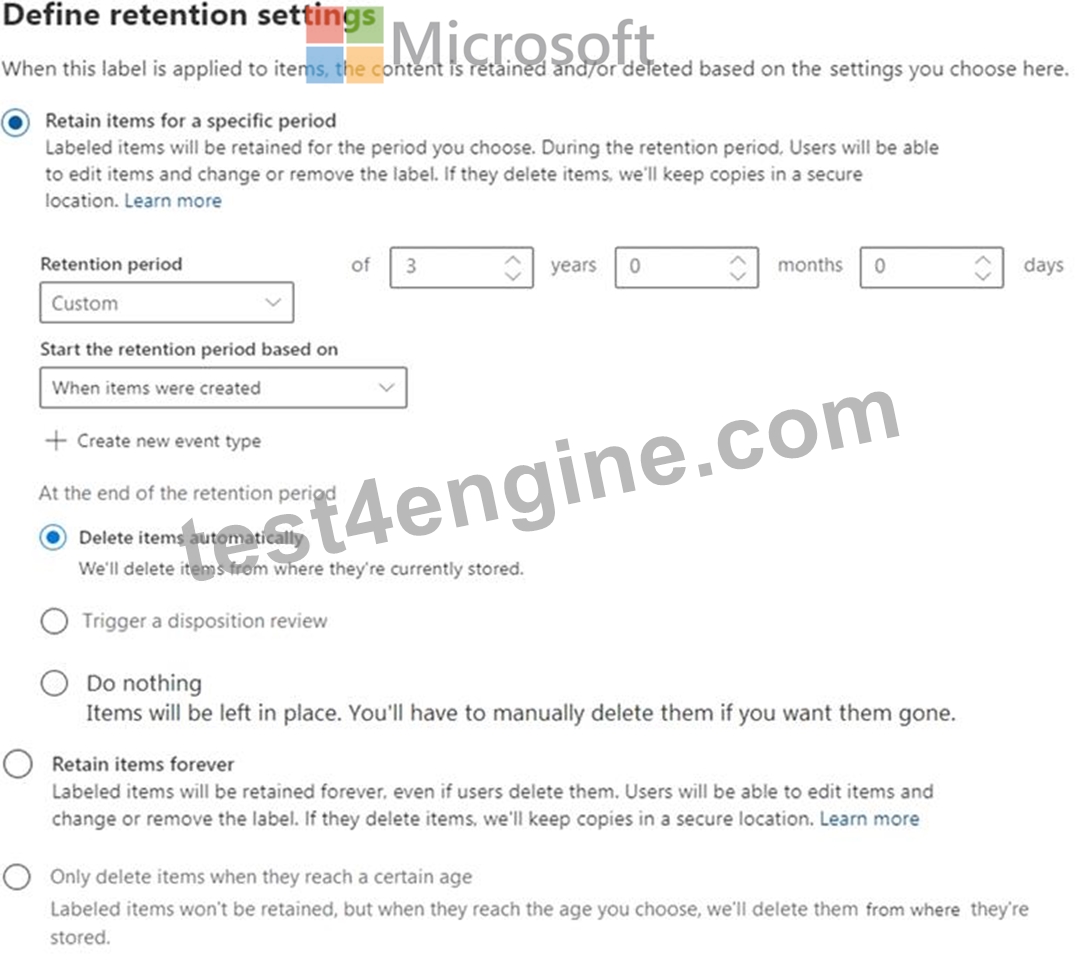
You need to ensure that documents that have Label1 applied are deleted three years after the end of your company's fiscal year.
What should you do?
- A. Select Only delete items when they reach a certain age.
- B. Create a new event type.
- C. Set At the ends of the retention period to Trigger a disposition review.
- D. Modify the Retention period setting.
Answer: B
Explanation:
https://docs.microsoft.com/en-us/microsoft-365/compliance/event-driven-retention?view=o365-worldwide
NEW QUESTION 52
How many files in Site2 will be visible to User1 and User2 after you turn on DLPpolicy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.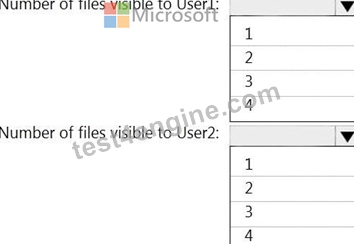
Answer:
Explanation: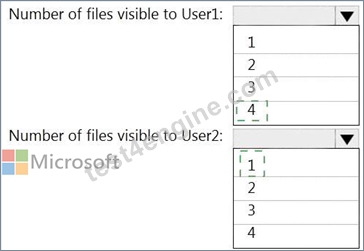
Explanation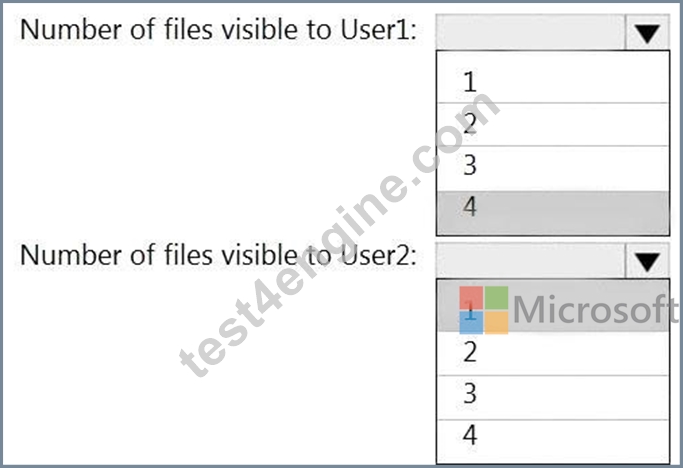
Reference:
https://social.technet.microsoft.com/wiki/contents/articles/36527.implement-data-loss-prevention-dlp-in-sharepo
NEW QUESTION 53
......
SC-400 Exam Dumps - PDF Questions and Testing Engine: https://www.test4engine.com/SC-400_exam-latest-braindumps.html
Latest SC-400 Exam Dumps for Pass Guaranteed: https://drive.google.com/open?id=1t25goJoiM3exyQ7ZUqT-hUgBkk-poieR