


Free Nov-2024 UPDATED Cisco 300-440 Certification Exam Dumps is Online
Cisco Exam 2024 300-440 Dumps Updated Questions
Cisco 300-440 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 19 
Refer to the exhibit. An engineer needs to configure a site-to-site IPsec VPN connection between an on-premises Cisco IOS XE router and Amazon Web Services (AWS). Which configuration command must be placed in the blank in the code to complete the tunnel configuration?
- A. tunnel source 192.10.10.10
- B. tunnel source 20.20.20.21
- C. address 192.10.10.10
- D. address 20.20.20.21
Answer: B
Explanation:
In the given scenario, an engineer is configuring a site-to-site IPsec VPN connection between an on-premises Cisco IOS XE router and AWS. The correct command to complete the tunnel configuration is "tunnel source
20.20.20.21". This command specifies the source IP address for the tunnel, which is essential for establishing a secure connection between two endpoints over the internet or another network1. References:
Configure IOS-XE Site-to-Site VPN Connection to Amazon Web Services - Cisco Community
[Security for VPNs with IPsec Configuration Guide, Cisco IOS XE Release 3S - Config
NEW QUESTION # 20
Refer to the exhibit.
Refer to the exhibits. An engineer must redistribute IBGP routes into OSPF to connect an on-premises network to a cloud provider. Which command must be configured on router R2?
- A. redistribute bgp 100 ospf 1
- B. bgp redistrlbute-lnternal
- C. redistribute ospf 1
- D. redistribute bgp 100 subnets
Answer: A
Explanation:
This command redistributes the routes learned from BGP AS100 into OSPF Area 1, which allows router R2 to advertise those routes to router R1 and connect the on-premises network to the cloud provider. The other options are incorrect because they either redistribute the wrong routes or use the wrong syntax5 .
I hope this helps you understand the question and the answer. If you have any other questions or requests, please let me know. I am always happy to help.
References: 1: Learning Plan: Designing and Implementing Cloud Connectivity v1.0 (ENCC 300-440) Exam Prep 2: Designing and Implementing Cloud Connectivity (ENCC) v1.0 3: Cisco Multiprotocol Label Switching 4: Exploring Cisco Cloud OnRamp for Colocation 5: ENCC: Configuring IPsec VPN from Cisco IOS XE to AWS : [Deploying Cisco IOS VTI-Based Point-to-Point IPsec VPNs]
NEW QUESTION # 21
An engineer must enable the OMP advertisement of BGP routes for a specific VRF instance on a Cisco IOS XE SD-WAN device. What should be configured after the global address-family ipv4 is configured?
- A. Enable bgp advertisement.
- B. Set the VRF-specific route advertisements.
- C. Enter sdwan mode.
- D. Disable bgp advertisement.
Answer: A
Explanation:
To enable the OMP advertisement of BGP routes for a specific VRF instance on a Cisco IOS XE SD-WAN device, the engineer must first configure the global address-family ipv4 and then enable bgp advertisement under the vrf definition. This will allow the device to advertise the BGP routes learned from the cloud provider to the OMP control plane, which will then distribute them to the other SD-WAN devices in the overlay network1 References := 1: Designing and Implementing Cloud Connectivity (ENCC) v1.0, Module 3: Implementing Cloud Connectivity, Lesson 3: Configuring IPsec VPN from Cisco IOS XE to AWS, Topic: Configuring BGP on the Cisco IOS XE Device, Page 3-24.
NEW QUESTION # 22
What is the role of service providers to establish private connectivity between on-premises networks and Google Cloud resources?
- A. provide end-to-end encryption for data transmission using native IPsec
- B. facilitate direct, dedicated network connections through Google Cloud Interconnect
- C. enable intelligent routing and dynamic path selection using software-defined networking
- D. accelerate content delivery through integration with Google Cloud CDN
Answer: B
Explanation:
The role of service providers to establish private connectivity between on-premises networks and Google Cloud resources is to facilitate direct, dedicated network connections through Google Cloud Interconnect.
Google Cloud Interconnect is a service that allows customers to connect their on-premises networks to Google Cloud through a service provider partner. This provides low latency, high bandwidth, and secure connectivity to Google Cloud services, such as Google Compute Engine, Google Cloud Storage, and Google BigQuery.
Google Cloud Interconnect also supports hybrid cloud scenarios, such as extending on-premises networks to Google Cloud regions, or connecting multiple Google Cloud regions together. Google Cloud Interconnect offers two types of connections: Dedicated Interconnect and Partner Interconnect. Dedicated Interconnect provides physical connections between the customer's network and Google's network at a Google Cloud Interconnect location. Partner Interconnect provides virtual connections between the customer's network and Google's network through a supported service provider partner. Both types of connections use VLAN attachments to establish private connectivity to Google Cloud Virtual Private Cloud (VPC) networks. References:
Designing and Implementing Cloud Connectivity (ENCC) v1.0
[Google Cloud Interconnect Overview]
[Google Cloud Interconnect Documentation]
NEW QUESTION # 23
Refer to the exhibit.
Which Cisco lKEv2 configuration brings up the IPsec tunnel between the remote office router and the AWS virtual private gateway?
- A.

- B.

- C.

Answer: A
Explanation:
Option C is the correct answer because it configures the IKEv2 profile with the correct match identity, authentication, and keyring parameters. It also configures the IPsecprofile with the correct transform set and lifetime parameters. Option A is incorrect because it does not specify the match identity remote address in the IKEv2 profile, which is required to match the AWS virtual private gateway IP address. Option B is incorrect because it does not specify the authentication pre-share in the IKEv2 profile, which is required to authenticate the IKEv2 peers using a pre-shared key. Option C also matches the configuration example provided by AWS1 and Cisco2 for setting up an IKEv2 IPsec site-to-site VPN between a Cisco IOS-XE router and an AWS virtual private gateway. References :=
1: AWS VPN Configuration Guide for Cisco IOS-XE
2: Configure IOS-XE Site-to-Site VPN Connection to Amazon Web Services
NEW QUESTION # 24 
Refer to the exhibit. These configurations are complete:
* Create an account in the Equinix portal.
* Associate the Equinix account with Cisco vManage.
* Configure the global settings for Interconnect Gateways.
Drag the prerequisite steps from the left onto the order on the right to configure a Cisco SD-WAN Cloud Interconnect with Equinix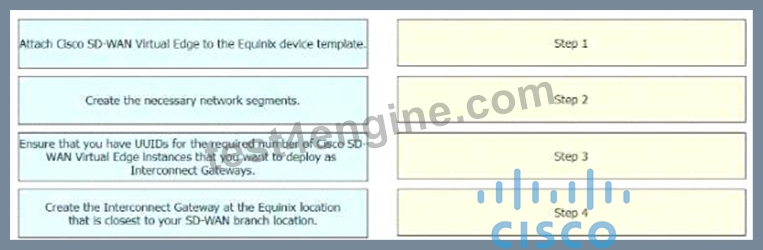
Answer:
Explanation:
Explanation:
The process of configuring a Cisco SD-WAN Cloud Interconnect with Equinix involves several steps.
Ensure that you have UUIDs for the required number of Cisco SD WAN Virtual Edge instances that you want to deploy as Interconnect Gateways: This is the first step where you ensure that you have the necessary UUIDs for the Cisco SD-WAN Virtual Edge instances that you want to deploy.
Create the necessary network segments: After ensuring the availability of UUIDs, you create the necessary network segments.
Attach Cisco SD-WAN Virtual Edge to the Equinix device template: After setting up the network segments, you attach the Cisco SD-WAN Virtual Edge to the Equinix device template.
Create the Interconnect Gateway at the Equinix location that is closest to your SD-WAN branch location: Finally, you create the Interconnect Gateway at the Equinix location that is closest to your SD-WAN branch location.
References :=
[Cisco SD-WAN Cloud Interconnect with Equinix]
[Cisco SD-WAN Cloud OnRamp for CoLocation Deployment Guide]
NEW QUESTION # 25
An engineer must configure a CLI add-on feature template in Cisco vManage for enhanced policy-based routing (ePBR) for IPv4. These configurations were deleted:
* licensing config enable false
* licensing config privacy hostname true
* licensing config privacy version false
* licensing config utility utility-enable true
Drag and drop the steps from the left onto the order on the right to complete the configuration.
Answer:
Explanation:
Explanation:
Step 1 = Click Configuration, select Templates, and then select Feature Templates. Step 2 = Click Add Template, select the device, and then click Select Template. Step 3 = Click CLI Add-On Template and enter the name and description. Step 4 = Paste the CLI configuration and then click Save.
The process of configuring a CLI add-on feature template in Cisco vManage for enhanced policy-based routing (ePBR) for IPv4 involves several steps1234.
Click Configuration, select Templates, and then select Feature Templates: This is the first step where you navigate to the Templates section in the Configuration menu of Cisco vManage1.
Click Add Template, select the device, and then click Select Template: In this step, you add a new template for the device1.
Click CLI Add-On Template and enter the name and description: After setting up the template, you select the CLI Add-On Template option, and then enter the name and description for the template1.
Paste the CLI configuration and then click Save: Finally, you paste the CLI configuration into the template and save the changes1.
References :=
CLI Add-On Feature Templates - Cisco
Cisco Catalyst SD-WAN Systems and Interfaces Configuration Guide, Cisco IOS XE Catalyst SD-WAN Release 17.x - CLI Add-On Feature Templates Cisco SD-WAN vSmart CLI Template - NetworkLessons.com CLI Templates for Cisco XE SD-WAN Routers
NEW QUESTION # 26
A company has multiple branch offices across different geographic locations and a centralized data center. The company plans to migrate Its critical business applications to the public cloud infrastructure that is hosted in Microsoft Azure. The company requires high availability, redundancy, and low latency for its business applications. Which connectivity model meets these requirements?
- A. site-to-site VPN with Azure VPN gateway
- B. hybrid connectivity with SD-WAN
- C. ExpressRoute with private peering using SDCI
- D. AWS Direct Connect with dedicated connections
Answer: C
Explanation:
The connectivity model that meets the requirements of high availability, redundancy, and low latency for the company's business applications is ExpressRoute with private peering using SDCI.
ExpressRoute is a service that provides a dedicated, private, and high-bandwidth connection between the customer's on-premises network and Microsoft Azure cloud network1.
Private peering is a type of ExpressRoute circuit that allows the customer to access Azure services that are hosted in a virtual network, such as virtual machines, storage, and databases2.
SDCI (Secure Data Center Interconnect) is a Cisco solution that enables secure and scalable connectivity between multiple data centers and cloud providers, using technologies such as MPLS, IPsec, and SD-WAN3.
By using ExpressRoute with private peering and SDCI, the company can achieve the following benefits:
High availability: ExpressRoute circuits are redundant and resilient, and can be configured with multiple service providers and locations for failover and load balancing1. SDCI also provides high availability by using dynamic routing protocols and encryption mechanisms to ensure optimal and secure path selection3.
Redundancy: ExpressRoute circuits can be paired together to form a redundant connection between the customer's network and Azure4. SDCI also supports redundancy by allowing multiple connections between data centers and cloud providers, using different transport technologies and service levels3.
Low latency: ExpressRoute circuits offer lower latency than public internet connections, as they bypass the congestion and variability of the internet1. SDCI also reduces latency by using MPLS and SD-WAN to optimize the performance and quality of service for the traffic between data centers and cloud providers3.
References:
What is Azure ExpressRoute?
Azure ExpressRoute peering
Cisco Secure Data Center Interconnect
ExpressRoute circuit and routing domain
NEW QUESTION # 27
Which method is used to create authorization boundary diagrams (ABDs)?
- A. identify only interconnected systems that are FedRAMP-authorized
- B. identify all tools as either external or internal to the boundary
- C. show all networks in CIDR notation only
- D. show only minor or small upgrade level software components
Answer: B
Explanation:
According to the FedRAMP Authorization Boundary Guidance document1, the method used to create authorization boundary diagrams (ABDs) is to identify all tools as either external orinternal to the boundary.
The ABD is a visual representation of the components that make up the authorization boundary, which includes all technologies, external and internal services, and leveraged systems and accounts for all federal information, data, and metadata that a Cloud Service Offering (CSO) is responsible for. The ABD should illustrate a CSP's scope of control over the system and show components or services that are leveraged from external services or controlled by the customer1. The other options are incorrect because they do not capture the full scope and details of the authorization boundary as required by FedRAMP. References := FedRAMP Authorization Boundary Guidance document1
NEW QUESTION # 28
Refer to the exhibit.
Drag and drop the steps from the left onto the order on the right to configure a site-to-site VPN connection between an on-premises Cisco IOS XE router and Amazon Web Services (AWS).
Answer:
Explanation:
Explanation:
Step 1 = Create a Customer Gateway (CGW) in AWS. Step 2 = Create a Virtual Private Gateway (VGW) in AWS. Step 3 = Create a site-to-site VPN connection in AWS. Step 4 = Configure the IOS XE router with the required IPsec VPN parameters and routing settings. Step 5 = Verify and test the VPN connection.
The process of configuring a site-to-site VPN connection between an on-premises Cisco IOS XE router and Amazon Web Services (AWS) involves several steps12.
Create a Customer Gateway (CGW) in AWS: This is the first step where you define the public IP address of your on-premises Cisco IOS XE router in AWS1.
Create a Virtual Private Gateway (VGW) in AWS: This involves creating a VGW and attaching it to the VPC in AWS1.
Create a site-to-site VPN connection in AWS: After setting up the CGW and VGW, you then create a site-to-site VPN connection in AWS. This involves specifying the CGW, VGW, and the static IP prefixes for your on-premises network1.
Configure the IOS XE router with the required IPsec VPN parameters and routing settings: After the AWS side is set up, you configure the on-premises Cisco IOS XE router with the required IPsec VPN parameters and routing settings2.
Verify and test the VPN connection: Finally, you verify and test the VPN connection to ensure that it is working correctly12.
References :=
Configure IOS-XE Site-to-Site VPN Connection to Amazon Web Services - Cisco Community SD-WAN Configuration Example: Site-to-site (LAN to LAN) IPSec between vEdge and Cisco IOS - Cisco Community
NEW QUESTION # 29
An engineer signs in to Cisco vManage and needs to configure a custom application with a Cisco SD-WAN centralized policy. Drag and drop the steps from the left onto the order on the right to complete the configuration.
Answer:
Explanation:
Explanation:
To configure a custom application with Cisco SD-WAN centralized policy, you need to follow these steps25:
Click Configuration, select Policies, and then select Centralized Policy.
Click Custom Options, select Centralized Policy, and then select Lists.
Click Custom Applications, and then select New Custom Application.
Enter a name for the application, enter the match criteria, and then click Add.
The process of configuring a custom application with a Cisco SD-WAN centralized policy using Cisco vManage involves several steps1.
Click Configuration, select Policies, and then select Centralized Policy: This is the first step where you navigate to the Policies section in the Configuration menu of Cisco vManage1.
Click Custom Options, select Centralized Policy, and then select Lists: In this step, you select the Custom Options, then select Centralized Policy, and finally select Lists1.
Click Custom Applications, and then select New Custom Application: After setting up the Lists, you click on Custom Applications and then select New Custom Application1.
Enter a name for the application, enter the match criteria, and then click Add: Finally, you enter a name for the application, specify the match criteria, and then click Add to complete the configuration1.
References :=
Cisco Catalyst SD-WAN Policies Configuration Guide, Cisco IOS XE
NEW QUESTION # 30
An engineer must configure cloud connectivity with Cisco Umbrella Secure Internet Gateway (SIG) in active/backup mode. The engineer already configured the SIG Credentials and SIG Feature Templates. Drag and drop the steps from the left onto the order on the right to complete the configuration.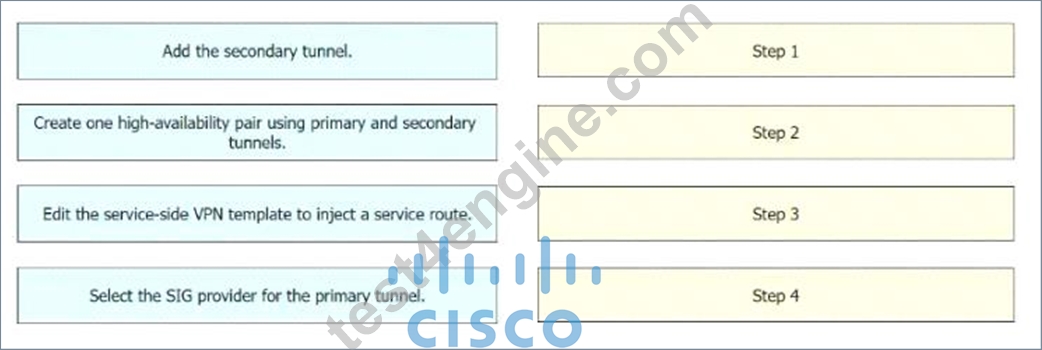
Answer:
Explanation:
Explanation:
The configuration of cloud connectivity with Cisco Umbrella Secure Internet Gateway (SIG) in active/backup mode involves several steps. After configuring the SIG Credentials and SIG Feature Templates, the engineer must:
Select the SIG provider for the primary tunnel: This is the first step in setting up the active/backup mode. The primary tunnel is the main connection path for the cloud connectivity.
Add the secondary tunnel: The secondary tunnel serves as a backup in case the primary tunnel fails. It ensures that the cloud connectivity remains uninterrupted even if there are issues with the primary tunnel.
Create one high-availability pair using primary and secondary tunnels: This step involves pairing the primary and secondary tunnels to create a high-availability pair. Thisensures that the cloud connectivity will switch over to the secondary tunnel seamlessly if the primary tunnel fails.
Edit the service-side VPN template to inject a service route: The final step involves modifying the VPN template on the service side to include a service route. This ensures that the traffic is correctly routed through the primary or secondary tunnel as needed.
References :=
Designing and Implementing Cloud Connectivity (ENCC) v1.01
Learning Plan: Designing and Implementing Cloud Connectivity v1.0 (ENCC 300-440) Exam Prep2 Configure Umbrella SIG Tunnels for Active/Backup or Active/Active Scenarios - Cisco3
NEW QUESTION # 31
An engineer is implementing a highly securemultitierapplication in AWS that includes S3. RDS, and some additional private links. What is critical to keep the traffic safe?
- A. gateway load balancers and specific routing policies
- B. specific routing and bucket policies
- C. EC2 super policies and specific routing policies
- D. VPC peering and bucket policies
Answer: B
Explanation:
A highly secure multitier application in AWS that includes S3, RDS, and some additional private links requires specific routing and bucket policies to keep the traffic safe. The reasons are as follows:
Specific routing policies are needed to ensure that the traffic between the tiers is routed through the private links, which provide secure and low-latency connectivity between AWS services and on-premises resources12. The private links can also prevent the exposure of the data and the application logic to the public internet12.
Bucket policies are needed to control the access to the S3 buckets that store the application data34. Bucket policies can specify the conditions under which the requests are allowed or denied, such as the source IP address, the encryption status, the request time, etc.34. Bucket policies can also enforce encryption in transit and at rest for the data in S334.
References :=
1: AWS PrivateLink
2: AWS PrivateLink FAQs
3: Using Bucket Policies and User Policies
4: Bucket Policy Examples
NEW QUESTION # 32
Which architecture model establishes internet-based connectivity between on-premises networks and AWS cloud resources?
- A. That relies on AWS Elastic Load Balancing (ELB) for traffic distribution and uses SSL/TLS encryption for secure data transmission.
- B. That uses Amazon CloudFrontfor caching and distributing content globally and uses HTTPS for secure data transfer.
- C. That establishes an iPsec VPN tunnel with Internet Key Exchange (IKE) for secure key negotiation and encrypted data transmission
- D. That employs AWS Direct Connect for a dedicated network connection and uses private IP addresses tor secure communication.
Answer: C
Explanation:
The architecture model that establishes internet-based connectivity between on-premises networks and AWS cloud resources is the one that establishes an iPsec VPN tunnel with Internet Key Exchange (IKE) for secure key negotiation and encrypted data transmission. This model is also known as the VPN CloudHub model12. It allows multiple remote sites to connect to the same virtual private gateway in AWS, creating a hub-and-spoke topology1. The VPN CloudHub model provides the following benefits12:
It enables secure communication between remote sites and AWS over the public internet, using encryption and authentication protocols such as IPsec and IKE.
It supports dynamic routing protocols such as BGP, which can automatically adjust the routing tables based on the availability and performance of the VPN tunnels.
It allows for redundancy and load balancing across multiple VPN tunnels, increasing the reliability and throughput of the connectivity.
It simplifies the management and configuration of the VPN connections, as each remote site only needs to establish one VPN tunnel to the virtual private gateway in AWS, rather than multiple tunnels to different VPCs or regions.
The other options are not correct because they do not establish internet-based connectivity between on-premises networks and AWS cloud resources. Option B relies on AWS Elastic Load Balancing (ELB) for traffic distribution and uses SSL/TLS encryption for secure data transmission. However, ELB is a service that distributes incoming traffic across multiple targets within a VPC, not across different networks3. Option C employs AWS Direct Connect for a dedicated network connection and uses private IP addresses for secure communication. However, AWS Direct Connect is a service that establishes a private connection between on-premises networks and AWS, bypassing the public internet4. Option D uses Amazon CloudFront for caching and distributing content globally and uses HTTPS for secure data transfer. However, Amazon CloudFront is a service that delivers static and dynamic web content to end users, not to on-premises networks5.
References:
1: Designing and Implementing Cloud Connectivity (ENCC, Track 1 of 5)
2: Cisco ASA Site-to-Site VPN
3: What Is Elastic Load Balancing?
4: What is AWS Direct Connect?
NEW QUESTION # 33 

Refer to the exhibits. An engineer must redistribute OSPF internal routes into BGP to connect an on-premises network to a cloud provider. Which two commands should the engineer run on router R2? (Choose two.)
- A. router bgp 100
- B. redistribute ospf 100
- C. redistribute ospf 1
- D. redistribute bgp 100
- E. router ospf 1
Answer: A,C
Explanation:
To redistribute OSPF internal routes into BGP for connecting an on-premises network to a cloud provider, the engineer should run the commands "router bgp 100" and "redistribute ospf 1" on router R2. The command
"router bgp 100" is used to create a BGP routing process with AS number 100. The command "redistribute ospf 1" is used to redistribute OSPF routes from process ID 1 into BGP. References: = I need to access the specific content of Designing and Implementing Cloud Connectivity (ENCC) v1.0 from Cisco's official resources to provide exact references. However, I don't have direct access to external databases or resources, including the Cisco ENCC course materials. I recommend referring to the ENCC course materials for the most accurate and detailed information. Please note that this answer is based on general networking principles and may not reflect the specific content of the ENCC course. Always refer to the official course materials for the most accurate information.
NEW QUESTION # 34
A company with multiple branch offices wants a connectivity model to meet its network architecture requirements. The company focuses on ensuring low latency and efficient routing for its critical business applications. Which connectivity model meets these requirements?
- A. hub-and-spoke topology with SD-WAN technology, using dynamic routing and OSPF as the routing protocol
- B. star topology with internet-based VPN connections and static routing
- C. fully meshed topology with SD-WAN technology, using dynamic routing and BGP as the routing protocol
- D. point-to-point topology using dedicated leased lines and static routing
Answer: C
Explanation:
A fully meshed topology with SD-WAN technology, using dynamic routing and BGP as the routing protocol, meets the requirements of the company because it provides the following benefits:
It allows direct and secure connectivity between any two branch offices, without the need for a central hub or intermediary devices12. This reduces the latency and improves the performance of the critical business applications.
It leverages SD-WAN technology to optimize the traffic flow and application quality of service (QoS) across the WAN13. SD-WAN can dynamically select the best path for each application based on the network conditions and policies13. SD-WAN can also provide redundancy, security, and visibility for the WAN13.
It uses dynamic routing and BGP as the routing protocol to exchange routing information and establish connectivity between the branch offices14. BGP is a scalable and flexible protocol that can support multiple address families, such as IPv4 and IPv6, and multiple routing policies, such as local preference and route filtering14. BGP can also enable seamless integration with the cloud service providers (CSPs) and internet service providers (ISPs)14.
References :=
1: Designing and Implementing Cloud Connectivity (ENCC, Track 1 of 5) (Cisco U. login required)
2: Cisco SD-WAN Design Guide
NEW QUESTION # 35
......
Cisco Certified 300-440 Dumps Questions Valid 300-440 Materials: https://www.test4engine.com/300-440_exam-latest-braindumps.html
Get The Most Updated 300-440 Dumps To CCNP Enterprise Certification: https://drive.google.com/open?id=13RpSe3_dpk4bKnzFJZcMm_BherTGNs0L