


[Jan 01, 2022] Fully Updated CS0-002 Dumps - 100% Same Q&A In Your Real Exam
Latest CS0-002 Exam Dumps - Valid and Updated Dumps
Prerequisites for Taking the CompTIA CySA+ Certification Exam
CS0-002 has no strict requirements. Anyone, regardless of their knowledge level, can apply to take the test. However, CompTIA does recommend that you have a minimum of 4 years’ experience in the cybersecurity field. Also, the candidates should possess the CompTIA Network+ or CompTIA Security+ certificate or understand everything covered by them.
NEW QUESTION 115
A security analyst is reviewing packet captures from a system that was compromised. The system was already isolated from the network, but it did have network access for a few hours after being compromised. When viewing the capture in a packet analyzer, the analyst sees the following:
Which of the following can the analyst conclude?
- A. The system is scanning ajgidwle.com for PII.
- B. The system is running a DoS attack against ajgidwle.com.
- C. Data is being exfiltrated over DNS.
- D. Malware is attempting to beacon to 128.50.100.3.
Answer: A
NEW QUESTION 116
For machine learning to be applied effectively toward security analysis automation, it requires
__________.
- A. a multicore, multiprocessor system.
- B. a threat feed API.
- C. relevant training data.
- D. anomalous traffic signatures.
Answer: D
NEW QUESTION 117
A security analyst discovers a vulnerability on an unpatched web server that is used for testing machine learning on Bing Data sets. Exploitation of the vulnerability could cost the organization $1.5 million in lost productivity. The server is located on an isolated network segment that has a 5% chance of being compromised. Which of the following is the value of this risk?
- A. $1.5 million
- B. $75.000
- C. $300.000
- D. $1.425 million
Answer: B
NEW QUESTION 118
A security analyst is trying to determine if a host is active on a network. The analyst first attempts the following: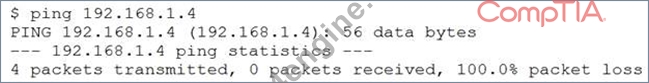
The analyst runs the following command next: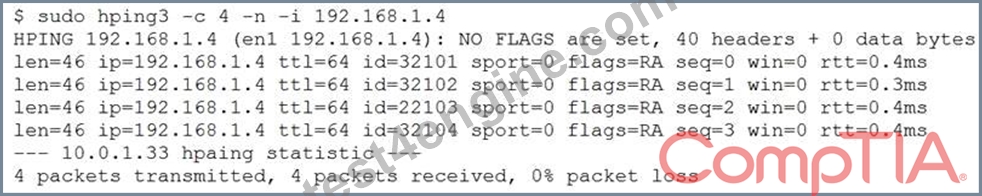
Which of the following would explain the difference in results?
- A. hping3 is returning a false positive.
- B. The original ping command needed root permission to execute.
- C. The routing tables for ping and hping3 were different.
- D. ICMP is being blocked by a firewall.
Answer: D
NEW QUESTION 119
A security analyst is investigating a malware infection that occurred on a Windows system.
The system was not connected to a network and had no wireless capability Company policy prohibits using portable media or mobile storage.
The security analyst is trying to determine which user caused the malware to get onto the system.
Which of the following registry keys would MOST likely have this information?
- A.

- B.

- C.

- D.

Answer: A
NEW QUESTION 120
A cyber incident response team finds a vulnerability on a company website that allowed an attacker to inject malicious code into its web application. There have been numerous unsuspecting users visiting the infected page, and the malicious code executed on the victim's browser has led to stolen cookies, hijacked sessions, malware execution, and bypassed access control. Which of the following exploits is the attacker conducting on the company's website?
- A. Privilege escalation
- B. Rootkit
- C. Cross-site scripting
- D. Logic bomb
Answer: C
NEW QUESTION 121
A security analyst is reviewing the following log after enabling key-based authentication.
Given the above information, which of the following steps should be performed NEXT to secure the system?
- A. Disable password authentication for SSH.
- B. Disable SSHv1.
- C. Disable remote root SSH logins.
- D. Disable anonymous SSH logins.
Answer: A
NEW QUESTION 122
A cybersecurity analyst needs to determine whether a large file named access log from a web server contains the following loC:
../../../../bin/bash
Which of the following commands can be used to determine if the string is present in the log?
- A. echo access.log | grep "../../../../bin/bash"
- B. grep "../../../../bin/bash" 1 cat access.log
- C. grep "../../../. ./bin/bash" < access.log
- D. cat access.log > grep "../../../ ../bin/bash"
Answer: C
NEW QUESTION 123
A security analyst is investigating a malware infection that occurred on a Windows system.
The system was not connected to a network and had no wireless capability Company policy prohibits using portable media or mobile storage.
The security analyst is trying to determine which user caused the malware to get onto the system.
Which of the following registry keys would MOST likely have this information?
- A.

- B.

- C.

- D.

Answer: C
NEW QUESTION 124
An analyst was testing the latest version of an internally developed CRM system. The analyst created a basic user account. Using a few tools in Kali's latest distribution, the analyst was able to access configuration files, change permissions on folders and groups, and delete and create new system objects. Which of the following techniques did the analyst use to perform these unauthorized activities?
- A. Input injection
- B. Privilege escalation
- C. Impersonation
- D. Directory traversal
Answer: D
NEW QUESTION 125
Which of the following software security best practices would prevent an attacker from being able to run arbitrary SQL commands within a web application? (Choose two.)
- A. Data protection
- B. Authentication
- C. Parameterized queries
- D. Output encoding
- E. Input validation
- F. Session management
Answer: C,E
NEW QUESTION 126
An organization has recently found some of its sensitive information posted to a social media site.
An investigation has identified large volumes of data leaving the network with the source traced back to host 192.168.1.13. An analyst performed a targeted Nmap scan of this host with the results shown below: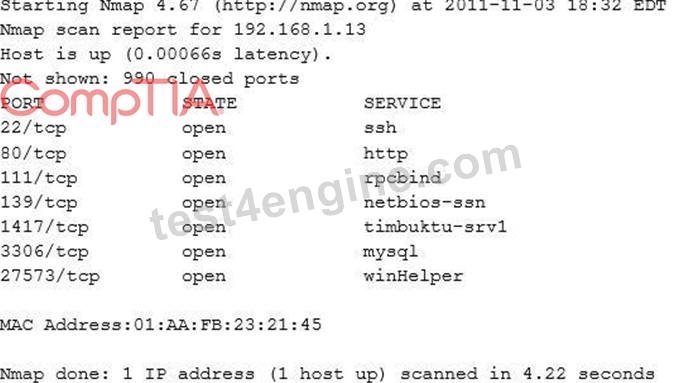
Subsequent investigation has allowed the organization to conclude that all of the well-known, standard ports are secure. Which of the following services is the problem?
- A. rpcbind
- B. mysql
- C. timbuktu-serv1
- D. winHelper
- E. ssh
Answer: C
NEW QUESTION 127
A security analyst reviews a recent network capture and notices encrypted inbound traffic on TCP port 465 was coming into the company's network from a database server. Which of the following will the security analyst MOST likely identify as the reason for the traffic on this port?
- A. Someone has configured an unauthorized SMTP application over SSL
- B. The server is receiving a secure connection using the new TLS 1.3 standard
- C. The traffic is common static data that Windows servers send to Microsoft
- D. A connection from the database to the web front end is communicating on the port
Answer: A
NEW QUESTION 128
A cybersecurity analyst is responding to an incident. The company's leadership team wants to attribute the incident to an attack group. Which of the following models would BEST apply to the situation?
- A. MITRE ATT&CK
- B. Diamond Model of Intrusion Analysis
- C. Intelligence cycle
- D. Kill chain
Answer: D
NEW QUESTION 129
Which of the following systems would be at the GREATEST risk of compromise if found to have an open vulnerability associated with perfect forward secrecy?
- A. Endpoints
- B. Virtual hosts
- C. SIEM
- D. Layer 2 switches
- E. VPN concentrators
Answer: E
NEW QUESTION 130
Which of the following could be directly impacted by an unpatched vulnerability in vSphere ESXi?
- A. The organization's virtual infrastructure
- B. The organization's VPN
- C. The organization's physical routers
- D. The organization's mobile devices
Answer: A
NEW QUESTION 131
A security professional is analyzing the results of a network utilization report. The report includes the following information:
Which of the following servers needs further investigation?
- A. mrktg.file.srvr.02
- B. hr.dbprod.01
- C. web.srvr.03
- D. R&D.file.srvr.01
Answer: B
NEW QUESTION 132
An organization has the following risk mitigation policy:
Risks with a probability of 95% or greater will be addressed before all others regardless of the impact.
All other prioritization will be based on risk value.
The organization has identified the following risks: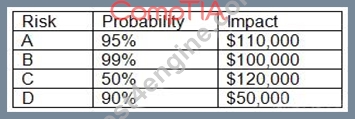
Which of the following is the order of priority for risk mitigation from highest to lowest?
- A. D, A, B, C
- B. A, B, D, C
- C. D, A, C, B
- D. A, B, C, D
Answer: C
NEW QUESTION 133
A small organization has proprietary software that is used internally. The system has not been well maintained and cannot be updated with the rest of the environment Which of the following is the BEST solution?
- A. Only allow access to the system via a jumpbox
- B. Implement MFA on the specific system.
- C. Virtualize the system and decommission the physical machine.
- D. Remove it from the network and require air gapping.
Answer: C
NEW QUESTION 134
A security analyst receives an alert that highly sensitive information has left the company's network Upon investigation, the analyst discovers an outside IP range has had connections from three servers more than 100 times m the past month.
The affected servers are virtual machines.
Which of the following is the BEST course of action?
- A. Disconnect the affected servers from the network, use the virtual machine console to access the systems, determine which information has left the network, find the security weakness, and remediate
- B. Report the data exfiltration to management take the affected servers offline, conduct an antivirus scan, remediate all threats found, and return the servers to service.
- C. Shut down the servers as soon as possible, move them to a clean environment, restart, run a vulnerability scanner to find weaknesses determine the root cause, remediate, and report
- D. Determine if any other servers have been affected, snapshot any servers found, determine the vector that was used to allow the data exfiltration. fix any vulnerabilities, remediate, and report.
Answer: C
NEW QUESTION 135
Because some clients have reported unauthorized activity on their accounts, a security analyst is reviewing network packet captures from the company's API server. A portion of a capture file is shown below:
POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.s/soap/envelope/"><s:Body><GetIPLocation+xmlns="http://tempuri.org/">
<request+xmlns:a="http://schemas.somesite.org"+xmlns:i="http://www.w3.org/2001/ XMLSchema-instance"></s:Body></s:Envelope> 192.168.1.22 - - api.somesite.com 200
0 1006 1001 0 192.168.1.22
POST /services/v1_0/Public/Members.svc/soap <<a:Password>Password123</
a:Password><a:ResetPasswordToken+i:nil="true"/>
<a:ShouldImpersonatedAuthenticationBePopulated+i:nil="true"/
><a:Username>[email protected]</a:Username></request></Login></s:Body></ s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 11558 1712 2024 192.168.4.89 POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.xmlsoap.org/soap/envelope/"><s:Body><GetIPLocation+xmlns="http:// tempuri.org/"> <a:IPAddress>516.7.446.605</a:IPAddress><a:ZipCode+i:nil="true"/
></request></GetIPLocation></s:Body></s:Envelope> 192.168.1.22 - -
api.somesite.com 200 0 1003 1011 307 192.168.1.22
POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http:// schemas.xmlsoap.org/soap/envelope/"><s:Body><IsLoggedIn+xmlns="http:// tempuri.org/"> <request+xmlns:a="http://schemas.datacontract.org/2004/07/ somesite.web+xmlns:i="http://www.w3.org/2001/XMLSchema- instance"><a:Authentication>
<a:ApiToken>kmL4krg2CwwWBan5BReGv5Djb7syxXTNKcWFuSjd</
a:ApiToken><a:ImpersonateUserId>0</a:ImpersonateUserId><a:LocationId>161222</ a:LocationId> <a:NetworkId>4</a:NetworkId><a:ProviderId>''1=1</ a:ProviderId><a:UserId>13026046</a:UserId></a:Authentication></request></ IsLoggedIn></s:Body></s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 1378
1209 48 192.168.4.89
Which of the following MOST likely explains how the clients' accounts were compromised?
- A. A SQL injection attack was carried out on the server.
- B. An XSS scripting attack was carried out on the server.
- C. The clients' authentication tokens were impersonated and replayed.
- D. The clients' usernames and passwords were transmitted in cleartext.
Answer: C
NEW QUESTION 136
In the development stage of the incident response policy, the security analyst needs to determine the stakeholders for the policy. Who of the following would be the policy stakeholders?
- A. Human resources, legal, public relations, management
- B. IT, human resources, security administrator, finance
- C. Chief information Officer (CIO), Chief Executive Officer, board of directors, stockholders
- D. Public information officer, human resources, audit, customer service
Answer: C
NEW QUESTION 137
A security analyst gathered forensics from a recent intrusion in preparation for legal proceedings.
The analyst used EnCase to gather the digital forensics, cloned the hard drive, and took the hard drive home for further analysis. Which of the following did the security analyst violate?
- A. Virtualization
- B. Hashing procedures
- C. Chain of custody
- D. Cloning procedures
Answer: C
NEW QUESTION 138
......
Free Sales Ending Soon - 100% Valid CS0-002 Exam: https://www.test4engine.com/CS0-002_exam-latest-braindumps.html
Verified CS0-002 Exam Questions Certain Success: https://drive.google.com/open?id=1qy5ep_3iOdfKQwxvhIAKI4h05kktnreN