


Latest [Mar 26, 2023] Real Microsoft AZ-720 Exam Dumps Questions
AZ-720 Dumps To Pass Microsoft Certified: Azure Support Engineer for Connectivity Specialty Exam in One Day (Updated 82 Questions)
Microsoft AZ-720 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
| Topic 12 |
|
| Topic 13 |
|
| Topic 14 |
|
NEW QUESTION 12
A company uses Azure AD Connect. The company plans to implement self-service password reset (SSPR).
An administrator receives an error that password writeback cloud not be enabled during the Azure AD
Connect configuration. The administrator observes the following event log error:
Error getting auth token
You need to resolve the issue.
Solution: Disable password writeback and then enable password writeback.
Does the solution meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 13
A company uses Azure Active Directory (Azure AD) with Azure role-based access control (RBAC) for access to resources.
Some users report that they are unable to grant RBAC roles to other users.
You need to troubleshoot the issue.
How should you complete the Azure Monitor query?
Answer:
Explanation:
NEW QUESTION 14
A company uses an Azure Backup agent to back up specific files and folder from an Azure virtual machine
(VM) and an on-premises VM.
An administrator reports that the backup job fails on both VMs. Errors are returned in Microsoft Azure
Recovery Services (MARS).
You need to troubleshoot the backup issues.
Which troubleshooting solution should you use?
Answer:
Explanation:
NEW QUESTION 15
A company enables just-in-time (JIT) virtual machine (VM) access in Azure.
An administrator observes a list of VMs on the Unsupported tab of the JIT VM access page in the Microsoft
Defender for Cloud portal.
You need to determine why some VMs are not supported for JIT VM access.
What should you conclude?
- A. The administrator does not have the SecurityReader role.
- B. The administrator is using the Microsoft Defender for Cloud free tier.
- C. The VMs were recently provisioned by using an Azure Resource Manager deployment.
- D. The VMs were provisioned by using a classic deployment.
Answer: D
NEW QUESTION 16
A company plans to implement ExpressRoute by using the provider connectivity model.
The company creates an ExpressRoute circuit. You are unable to connect to resources through the circuit.
You need to determine the provisioning state of the service provider.
Which PowerShell cmdlet should you run?
- A. Get-AzExpressRouteCircuitARPTable
- B. Get-AzExpressRouteCircuitRouteTable
- C. Get-AzExpressRouteCircuitPeeringConfig
- D. Get-AzExpressRouteCircuit
- E. Get-AzExpressRouteCircuitConnectionConfig
Answer: E
NEW QUESTION 17
A company uses Azure Backup Agent to back up specific files and folders from an on-premises virtual machine (VM).
An administrator reports that the backup job is transferring files slowly. You determine that the backup job is verifying changes in directories by scanning the entire volume.
You need to determine the state of the backup job.
In which state will the backups occur?
Answer:
Explanation:
NEW QUESTION 18
A company uses Azure Site Recovery (ASR) to replicate and recover Azure virtual machines (VM) between Azure regions.
An administrator receives the following warning from ASR about a VM that uses P10 disks: Data change rate beyond supported limits You add OS Disk Write Bytes/Sec and Data Disk Write Bytes/Sec to the list of metrics for monitoring. You discover that the VM consistently has a data churn of greater than 8 MB/s but less than 10 MB/s.
You need to resolve the issue.
What should you do?
- A. Create a network service endpoint in a virtual network.
- B. Uninstall the Volume Shadow Copy Service (VSS) Provider service.
- C. Use AzCopy to upload data to a cache storage account.
- D. Upgrade the target storage disk.
Answer: D
NEW QUESTION 19
A company connects their on-premises network by using Azure VPN Gateway. The on-premises environment includes three VPN devices that separately tunnel to the gateway by using Border Gateway Protocol (BGP).
A new subnet should be unreachable from the on-premises network.
You need to implement a solution.
Solution: Configure subnet delegation.
Does the solution meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 20
A company deploys the Azure Application Gateway Web Application Firewall (WAF) to protect their web applications.
Users in a remote office location report the following issues:
Unable to access part of a web application.
Part of the web application is failing to load.
Parts of the web application has activities that are not performing as expected.
You need to troubleshoot the issue.
Which diagnostic log should you review?
- A. Azure Activity
- B. Access
- C. Firewall
- D. Performance
Answer: A
NEW QUESTION 21
A company has an Azure Active Directory (Azure AD) tenant. The company deploys Azure AD Connect to
synchronize objects from their Active Directory Domain Services (AD DS) domain.
You observe that AD DS objects are not synchronizing to Azure AD.
You need to verify that the staging mode is enabled.
What should you do?
- A. Review the history for the Azure AD Connect sync scheduled task.
- B. Run this PowerShell cmdlet: Get-ADSyncConnetorRunStatus
- C. Run this PowerShell cmdlet: Get-ADSyncScheduler
- D. Review the triggers for the Azure AD Connect sync scheduled task.
Answer: C
NEW QUESTION 22
A company migrates an on-premises Windows virtual machine (VM) to Azure. An administrator enables backups for the VM by using the Azure portal.
The company reports that the Azure VM backup job is failing.
You need to troubleshoot the issue.
What should you do?
- A. Enable replication and create a recovery plan for the backup vault.
- B. Configure the retention range of the current backup policy for the VM.
- C. Install the VM guest agent with administrative permissions.
- D. Create a new manual backup in Backup center.
- E. Run chkdsk on the VM.
Answer: C
NEW QUESTION 23
A company migrates existing Ubuntu Linux servers from their on-premises vSphere infrastructure to Azure.
The virtual machines (VMs) are experiencing a low network throughput of 20 Mbps. The VMs are expected to sustain 300 Mbps.
You need to ensure that the VMs are compatible with Azure.
Which change should you make?
- A. Install a kernel name that ends with -azure.
- B. Increase the TCP buffers and window size kernel parameters.
- C. Redeploy the VM with Accelerated Networking enabled.
- D. Configure the network interfaces to 1000 Mbps/full duplex.
Answer: D
NEW QUESTION 24
A company deploys an Azure Firewall. The company reports the following log entry:
For each of the following questions, select Yes or No.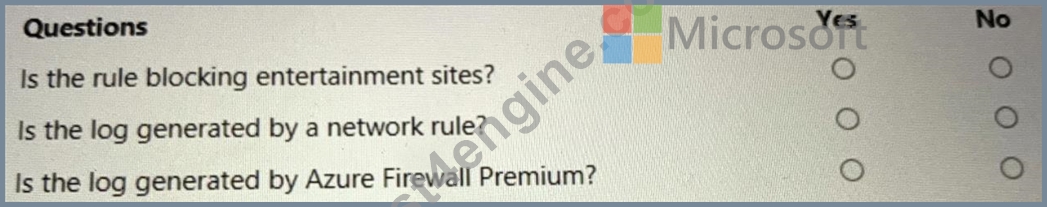
Answer:
Explanation: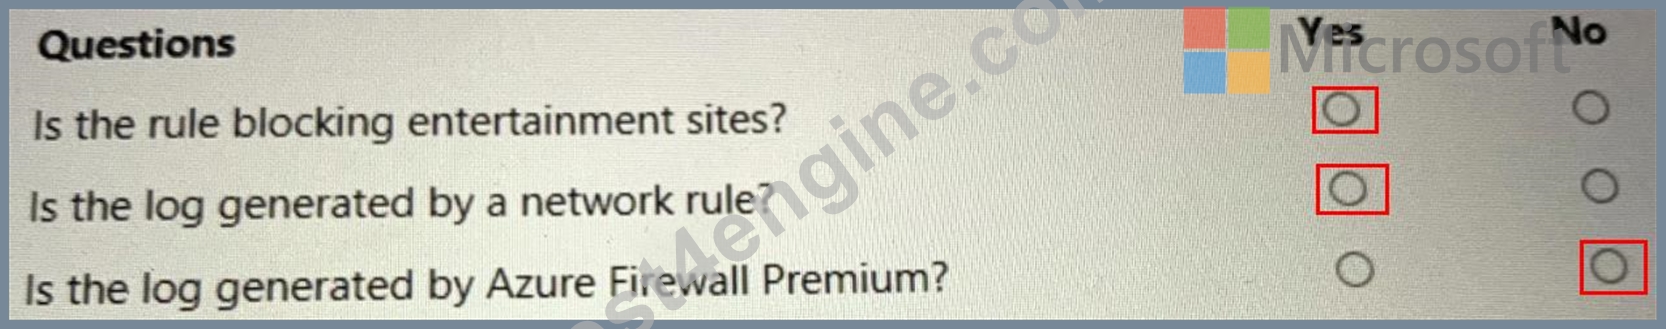
NEW QUESTION 25
A company uses Azure Active Directory (Azure AD) for authentication. The company synchronizes Azure AD with an on-premises Active Directory domain.
The company reports that an Azure AD object fails to sync.
You need to determine which objects are not syncing.
Which troubleshooting steps should you use to diagnose the failure?
Answer:
Explanation: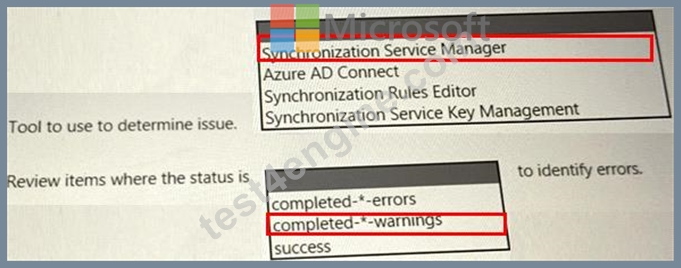
NEW QUESTION 26
A company has an Azure Virtual Network gateway named VNetGW1. The company enables point-to-site connectivity on VNetGW1. An administrator configures VNetGW1 for the following:
OpenVPN for the tunnel type.
Azure certificate for the authentication type.
Users receive a certificate mismatch error when connecting by using a VPN client.
You need to resolve the certificate mismatch error.
What should you do?
- A. Install an IKEv2 VPN client on the user's computers.
- B. Reissue the client certificate with client authentication enabled.
- C. Configure preshared key for authentication on the VPN profile.
- D. Reissue the client certificate with server authentication enabled.
Answer: D
NEW QUESTION 27
A company attempts to implement just-in-time (JIT) access for a virtual machine (VM) named VM1.
The company reports that they are unable to complete the process.
You need to implement JIT access and test the deployment.
Which PowerShell cmdlets should you run?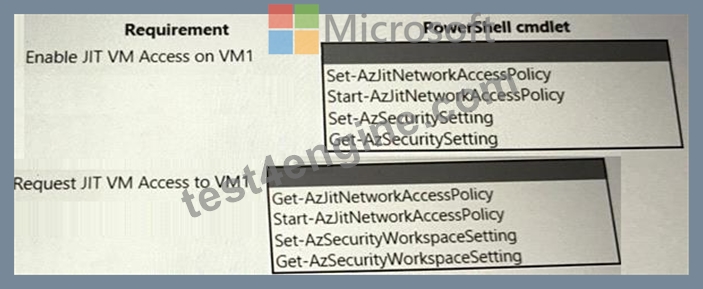
Answer:
Explanation: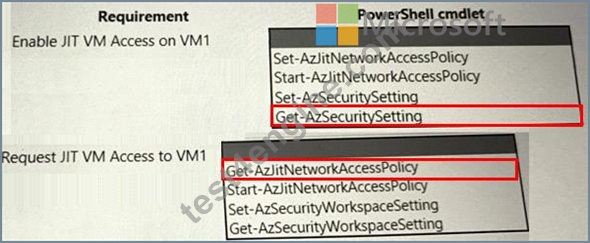
NEW QUESTION 28
A customer creates an Azure resource group named RG1 in the East US region. RG1 contains the following resources:
The customer performs the following tasks:
Create a private endpoint for sqlsrv1 in subnet2 with the private IP address of 192.168.2.100.
Create a private DNS zone named privatelink.database.windows.net by using a single A record named sqlsvr1 and the IP address 192.168.2.100.
Disable public access by using the public endpoint for sqlsvr1.
The customer reports that connections from VM1 to DB1 are failing. The solution must allow connections from VM1 to DB1 without making platform-level changes.
You need to troubleshoot and resolve the issue.
What should you do?
Answer:
Explanation: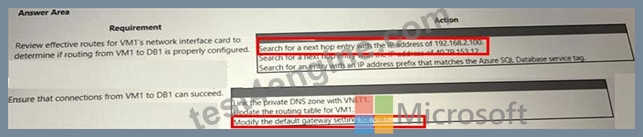
NEW QUESTION 29
A company has virtual machines (VMs) in the following Azure regions:
* West Central US
* Australia East
The company uses ExpressRoute private peering to provide connectivity to VMs hosted on each region and
on-premises services.
The company implements global VNet peering between a VNet in each region. After configuring VNet
peering, VM traffic attempts to use ExpressRoute private peering.
You need to ensure that traffic uses global VNet peering instead of ExpressRoute private peering. The solution
must preserve existing on-premises connectivity to Azure VNets.
What should you do?
- A. Add a second VNet to the virtual machines and configure VNet peering between the VNets.
- B. Add a filter to the on-premises routers.
- C. Disable the ExpressRoute peering connections for one of the regions.
- D. Add a user-defined route to the subnets route table.
Answer: B
NEW QUESTION 30
A company configures an Azure site-to-site VPN between an on-premises network and an Azure virtual
network.
The company reports that after completing the configuration, the VPN connection cannot be established.
You need to troubleshoot the connection issue.
What should you do first?
- A. Verify the AzureClient.pfx file exists.
- B. Identify the shared key by running this PowerShell cmdlet:
Get-AzVirtualNetworkGatewayConnectionSharedKey. - C. Identify the shared key by running this PowerShell cmdlet:
Get-AzVirtualNetworkGatewayConnectionVpnDeviceConfigScript. - D. Verify the AzureRoot.cer file exists.
Answer: C
NEW QUESTION 31
A company enables just-in-time (JIT) virtual machine (VM) access in Azure.
An administrator observes a list of VMs on the Unsupported tab of the JIT VM access page in the Microsoft Defender for Cloud portal.
You need to determine why some VMs are not supported for JIT VM access.
What should you conclude?
- A. The administrator does not have the SecurityReader role.
- B. The administrator is using the Microsoft Defender for Cloud free tier.
- C. The administrator does not have permissions to request JIT access to the VMs.
- D. The VMs were provisioned by using a classic deployment.
Answer: D
NEW QUESTION 32
A company uses Azure Site Recovery (ASR) to replicate and recover Azure virtual machines (VM) between
Azure regions.
An administrator receives the following warning from ASR about a VM that uses P10 disks: Data change rate
beyond supported limits
You add OS Disk Write Bytes/Sec and Data Disk Write Bytes/Sec to the list of metrics for monitoring. You
discover that the VM consistently has a data churn of greater than 8 MB/s but less than 10 MB/s.
You need to resolve the issue.
What should you do?
- A. Create a network service endpoint in a virtual network.
- B. Uninstall the Volume Shadow Copy Service (VSS) Provider service.
- C. Use AzCopy to upload data to a cache storage account.
- D. Upgrade the target storage disk.
Answer: D
NEW QUESTION 33
A company deploys an Azure Virtual Network gateway. The company connects to the gateway by using a
site-to-site VPN connection.
The company's on-premises VPN gateway is reporting an issue with the Phase 1 proposal from the Azure
Virtual Network gateway.
You need to troubleshoot the issue by reviewing the logs.
Which log should you analyze?
- A. GatewayDiagnosticLog
- B. IKEDiagnosticLog
- C. P2SDiagnosticLog
- D. RouteDiagnosticLog
Answer: B
NEW QUESTION 34
A company has two virtual networks (VNets) that are configured to use peering. Several Azure virtual
machines are connected to each network. An on-premises network is connected to one of the VNets by using
Azure VPN Gateway.
An administrator reports that communication between applications across the VNets is failing.
You need to troubleshoot the issue.
Which two features can you use to achieve the goal?
- A. AzureNetworkWatchExtension
- B. Network Watcher topology
- C. Next hop
- D. IP flow verify
- E. NSG flow logs
Answer: C,D
NEW QUESTION 35
A company connects their on-premises network by using Azure VPN Gateway. The on-premises environment
includes three VPN devices that separately tunnel to the gateway by using Border Gateway Protocol (BGP).
A new subnet should be unreachable from the on-premises network.
You need to implement a solution.
Solution: Disable peering on the virtual network.
Does the solution meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 36
A company has an Azure Virtual Network gateway named VNetGW1. The company enables point-to-site
connectivity on VNetGW1. An administrator configures VNetGW1 for the following:
* OpenVPN for the tunnel type.
* Azure certificate for the authentication type.
Users receive a certificate mismatch error when connecting by using a VPN client.
You need to resolve the certificate mismatch error.
What should you do?
- A. Create a profile manually, add the server FQDN and reissue the client certificate.
- B. Reissue the client certificate with server authentication enabled.
- C. Install an IKEv2 VPN client on the user's computers.
- D. Reissue the client certificate with client authentication enabled.
Answer: A
NEW QUESTION 37
......
AZ-720 Exam Brain Dumps - Study Notes and Theory: https://www.test4engine.com/AZ-720_exam-latest-braindumps.html
100% Guaranteed Results AZ-720 Unlimited 82 Questions: https://drive.google.com/open?id=1s5UbJHyC3WvqND2xjOX_VpzvM-m0cw3_