


You choose to apply for EC-COUNCIL Certified Ethical Hacker because you know the society is full of competition and challenges. If you do not want EC-Council Certified Security Analyst (ECSA) exam to become your stumbling block, you should consider our EC-Council Certified Security Analyst (ECSA) test for engine or 412-79 VCE test engine. Our Test4Engine is the leading position in this line and offer high-quality software test engine which can help you go through your examination. If you have no confidence for the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) exam, our EC-Council Certified Security Analyst (ECSA) test for engine will be your best select.

We have three versions for each exam dumps that: PDF dumps, Soft test engine, and APP on-line test engine. Totally the APP on-line test for engine is the most popular. Most candidates think about 412-79 test for engine or EC-Council Certified Security Analyst (ECSA) VCE test engine, they will choose APP on-line test engine in the end. The APP on-line test engine has many functions below.
1. EC-Council Certified Security Analyst (ECSA) APP on-line test engine includes the exam practice questions and answers. You can practice whenever you want. 412-79 VCE test engine includes 80% or so questions & answers of the real test. It is the foundation for passing exam. Of course, the PDF dumps & Soft test engine also have this function. (EC-Council Certified Security Analyst (ECSA) test for engine)
2. EC-Council Certified Security Analyst (ECSA) APP on-line test engine can imitate the real test; it can set timed test, mark your performance and point out your mistakes. (412-79 test for engine) It is really like the real test. It is helpful for clearing up your nervousness before test. The soft test engine also has this function but the PDF dumps do not.(EC-Council Certified Security Analyst (ECSA) VCE test engine)
3. EC-Council Certified Security Analyst (ECSA) APP on-line test engine can be installed in all operate systems. You can download EC-Council Certified Security Analyst (ECSA) VCE test engine in your computers, iPhones, iWatch, MP4 or MP5 and so on. You can learn any time and any place you like. The soft test engine can just be installed in personal computers.
4. Statistically speaking, EC-Council Certified Security Analyst (ECSA) APP on-line test engine is also stable than the soft test engine. It is more powerful.
Besides, you may doubt about our service. Yes, we guarantee your money and information safety. We make sure that "No Pass, No Pay". Our EC-Council Certified Security Analyst (ECSA) test for engine can assist you go through the examination surely, meanwhile, our service will 100% satisfy you.
1. Our working time is 7*24, we will serve for you any time even on official holiday. You email or news about 412-79 test for engine will be replied in 2 hours. Your questions & problems will be solved in 2 hours. After payment, you will receive our EC-Council Certified Security Analyst (ECSA) test for engine & EC-Council Certified Security Analyst (ECSA) VCE test engine soon.
2. We have professional IT staff who updates exam simulator engine every day so that all 412-79 test for engine we sell out is latest & valid. Also we have a strict information system which can guarantee your information safety.
3. We support Credit Card payment so that your account and money will be safe certainly, you are totally worry-free shopping. We guarantee our EC-Council Certified Security Analyst (ECSA) test for engine will assist you go through the examination surely. If you fail the exam unluckily we will refund you all the money you paid us unconditionally in one week. You get what you pay for.
More details please feel free to contact with us, we are pleased to serve for you. Give me a chance, I send you a success. EC-Council Certified Security Analyst (ECSA) test for engine & 412-79 VCE test engine will indeed be the best helper for your EC-COUNCIL 412-79 exam. If you choose us, you will 100% pass the exam for sure.
EC-COUNCIL 412-79 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Network Penetration Testing - Internal | 10-12% | - LAN and Active Directory testing - Internal network enumeration - Local system and privilege escalation |
| Topic 2: Penetration Testing Scoping & Engagement | 5-7% | - Engagement boundaries - Risk assessment and impact analysis - Contract and agreement preparation |
| Topic 3: Open-Source Intelligence (OSINT) | 5-6% | - Web-based intelligence gathering - Social media and public data analysis - OSINT automation tools |
| Topic 4: Wireless & Mobile Penetration Testing | 6-8% | - Wi-Fi security assessment - Mobile application vulnerabilities - Bluetooth and radio protocol testing |
| Topic 5: Information Gathering Methodology | 8-10% | - DNS, WHOIS, and network enumeration - Footprinting and reconnaissance techniques - OSINT and passive information collection |
| Topic 6: Network Penetration Testing - External | 10-12% | - External vulnerability assessment - Firewall and perimeter testing - External reconnaissance and scanning |
| Topic 7: Analysis & Reporting | 8-10% | - Remediation recommendations - Vulnerability validation and risk ranking - Executive and technical report writing |
| Topic 8: Pre-Penetration Testing Steps | 7-9% | - Scope definition and rules of engagement - Test plan development - Legal and compliance considerations |
| Topic 9: Web Application Penetration Testing | 12-14% | - Authentication and session testing - Input validation and injection attacks - OWASP Top 10 vulnerabilities |
| Topic 10: Database Penetration Testing | 7-9% | - Database security controls - SQL injection techniques - Database enumeration and discovery |
| Topic 11: Cloud & Virtual Environment Testing | 6-8% | - Cloud service model security - Identity and access management in cloud - Virtualization infrastructure assessment |
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) Sample Questions:
Identify the correct formula for Return on Investment (ROI).
- A. ROI = ((Expected Returns + Cost of Investment) / Cost of Investment) * 100
- B. ROI = (Expected Returns Cost of Investment) / Cost of Investment
- C. ROI = ((Expected Returns - Cost of Investment) / Cost of Investment) * 100
- D. ROI = (Expected Returns + Cost of Investment) / Cost of Investment
Correct Answer: B 🗳️
Identify the type of authentication mechanism represented below: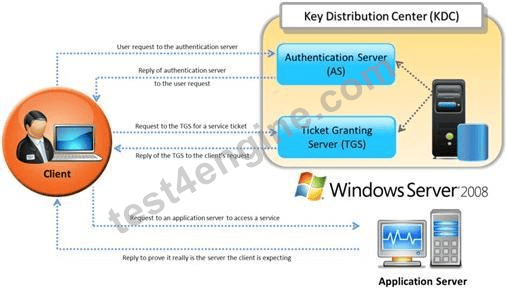
- A. LAN Manager Hash
- B. NTLMv2
- C. NTLMv1
- D. Kerberos
Correct Answer: D 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
Wireshark is a network analyzer. It reads packets from the network, decodes them, and presents them in an easy-to-understand format. Which one of the following is the command-line version of Wireshark, which can be used to capture the live packets from the wire or to read the saved capture files?
- A. Tshark
- B. Tcpdump
- C. Capinfos
- D. Idl2wrs
Correct Answer: C 🗳️
Amazon, an IT based company, conducts a survey on the usage of the Internet. They found that company employees spend most of the time at work surfing the web for their personal use and for inappropriate web site viewing. Management decide to block all such web sites using URL filtering software.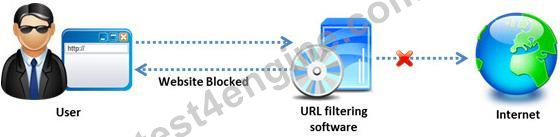
How can employees continue to see the blocked websites?
- A. Using authentication
- B. Using encryption
- C. Using session hijacking
- D. Using proxy servers
Correct Answer: D 🗳️
Which of the following is the objective of Gramm-Leach-Bliley Act?
- A. To set a new or enhanced standards for all U.S. public company boards, management and public accounting firms
- B. To certify the accuracy of the reported financial statement
- C. To ease the transfer of financial information between institutions and banks
- D. To protect the confidentiality, integrity, and availability of data
Correct Answer: C 🗳️


