


You choose to apply for EC-COUNCIL ECSA because you know the society is full of competition and challenges. If you do not want EC-Council Certified Security Analyst (ECSA) exam to become your stumbling block, you should consider our EC-Council Certified Security Analyst (ECSA) test for engine or ECSAv8 VCE test engine. Our Test4Engine is the leading position in this line and offer high-quality software test engine which can help you go through your examination. If you have no confidence for the EC-COUNCIL EC-Council Certified Security Analyst (ECSA) exam, our EC-Council Certified Security Analyst (ECSA) test for engine will be your best select.

We have three versions for each exam dumps that: PDF dumps, Soft test engine, and APP on-line test engine. Totally the APP on-line test for engine is the most popular. Most candidates think about ECSAv8 test for engine or EC-Council Certified Security Analyst (ECSA) VCE test engine, they will choose APP on-line test engine in the end. The APP on-line test engine has many functions below.
1. EC-Council Certified Security Analyst (ECSA) APP on-line test engine includes the exam practice questions and answers. You can practice whenever you want. ECSAv8 VCE test engine includes 80% or so questions & answers of the real test. It is the foundation for passing exam. Of course, the PDF dumps & Soft test engine also have this function. (EC-Council Certified Security Analyst (ECSA) test for engine)
2. EC-Council Certified Security Analyst (ECSA) APP on-line test engine can imitate the real test; it can set timed test, mark your performance and point out your mistakes. (ECSAv8 test for engine) It is really like the real test. It is helpful for clearing up your nervousness before test. The soft test engine also has this function but the PDF dumps do not.(EC-Council Certified Security Analyst (ECSA) VCE test engine)
3. EC-Council Certified Security Analyst (ECSA) APP on-line test engine can be installed in all operate systems. You can download EC-Council Certified Security Analyst (ECSA) VCE test engine in your computers, iPhones, iWatch, MP4 or MP5 and so on. You can learn any time and any place you like. The soft test engine can just be installed in personal computers.
4. Statistically speaking, EC-Council Certified Security Analyst (ECSA) APP on-line test engine is also stable than the soft test engine. It is more powerful.
Besides, you may doubt about our service. Yes, we guarantee your money and information safety. We make sure that "No Pass, No Pay". Our EC-Council Certified Security Analyst (ECSA) test for engine can assist you go through the examination surely, meanwhile, our service will 100% satisfy you.
1. Our working time is 7*24, we will serve for you any time even on official holiday. You email or news about ECSAv8 test for engine will be replied in 2 hours. Your questions & problems will be solved in 2 hours. After payment, you will receive our EC-Council Certified Security Analyst (ECSA) test for engine & EC-Council Certified Security Analyst (ECSA) VCE test engine soon.
2. We have professional IT staff who updates exam simulator engine every day so that all ECSAv8 test for engine we sell out is latest & valid. Also we have a strict information system which can guarantee your information safety.
3. We support Credit Card payment so that your account and money will be safe certainly, you are totally worry-free shopping. We guarantee our EC-Council Certified Security Analyst (ECSA) test for engine will assist you go through the examination surely. If you fail the exam unluckily we will refund you all the money you paid us unconditionally in one week. You get what you pay for.
More details please feel free to contact with us, we are pleased to serve for you. Give me a chance, I send you a success. EC-Council Certified Security Analyst (ECSA) test for engine & ECSAv8 VCE test engine will indeed be the best helper for your EC-COUNCIL ECSAv8 exam. If you choose us, you will 100% pass the exam for sure.
EC-COUNCIL ECSAv8 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Penetration Testing and Methodologies | - Introduction to Penetration Testing Methodologies - Network Penetration Testing – External - Web Application Penetration Testing - Perimeter Devices Penetration Testing - Open-Source Intelligence (OSINT) Methodology - Database Penetration Testing - Cloud Penetration Testing - Social Engineering Testing Methodology - Network Penetration Testing – Internal - Wireless Penetration Testing - Report Writing and Post-Testing Actions - Penetration Testing Scoping and Engagement |
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) Sample Questions:
The first and foremost step for a penetration test is information gathering. The main objective of this test is to gather information about the target system which can be used in a
malicious manner to gain access to the target systems.
Which of the following information gathering terminologies refers to gathering information through social engineering on-site visits, face-to-face interviews, and direct questionnaires?
- A. Active Information Gathering
- B. Anonymous Information Gathering
- C. Pseudonymous Information Gathering
- D. Open Source or Passive Information Gathering
Correct Answer: A 🗳️
Which of the following is an application alert returned by a web application that helps an attacker guess a valid username?
- A. Username or password incorrect
- B. Invalid username or password
- C. Account username was not found
- D. Incorrect password
Correct Answer: D 🗳️
A firewall's decision to forward or reject traffic in network filtering is dependent upon which of the following?
- A. Protocol used
- B. Source address
- C. Port numbers
- D. Destination address
Correct Answer: A 🗳️
Explanation: Only visible for Test4Engine members. You can sign-up / login (it's free).
You have compromised a lower-level administrator account on an Active Directory network of a small company in Dallas, Texas. You discover Domain Controllers through enumeration. You connect to one of the Domain Controllers on port 389 using Idp.exe. What are you trying to accomplish here?
- A. Establish a remote connection to the Domain Controller
- B. Enumerate MX and A records from DNS
- C. Enumerate domain user accounts and built-in groups
- D. Poison the DNS records with false records
Correct Answer: C 🗳️
What is a difference between host-based intrusion detection systems (HIDS) and network-based intrusion detection systems (NIDS)?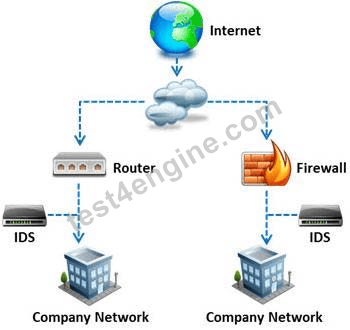
- A. NIDS are standalone hardware appliances that include network intrusion detection capabilities whereas HIDS consist of software agents installed on individual computers within the system.
- B. HIDS requires less administration and training compared to NIDS.
- C. NIDS are usually a more expensive solution to implement compared to HIDS.
- D. Attempts to install Trojans or backdoors cannot be monitored by a HIDS whereas NIDS can monitor and stop such intrusion events.
Correct Answer: A 🗳️


