


Dec 27, 2021 Step by Step Guide to Prepare for NSE7_EFW-6.4 Exam BrainDumps
NSE 7 Network Security Architect NSE7_EFW-6.4 Real Exam Questions and Answers FREE Updated on 2021
Introduction to Fortinet NSE7_EFQ-6.4: Fortinet NSE 7 - Enterprise Firewall 6.4 Exam
This exam is part of the preparation for the NSE 7 certification exam. The Fortinet Network Security Architect designation identifies your advanced skills in deploying, administering, and troubleshooting Fortinet security solutions. We recommend this certification for network and security professionals who are involved in the advanced administration and support of security infrastructures using Fortinet solutions. Visit the Fortinet NSE Certification Program page for information about certification requirements. You must pass a minimum of two Fortinet NSE 7 certification tests successfully:
- Fortinet NSE 7 - Advanced Threat Protection
- Fortinet NSE 7 - Secure Access
- Fortinet NSE 7 - SD-WAN
- Fortinet NSE 7 - Cloud Security
- Fortinet NSE 7 - Advanced Analytics
- Fortinet NSE 7 - Enterprise Firewall
- Fortinet NSE 7 - Enterprise Firewall 6.4 NSE7 EFW-6.4 exam test
The NSE 7 Network Security Architect designation recognizes your advanced skills and ability to deploy, administer, and troubleshoot Fortinet security solutions. To obtain certification, you must pass at least one Fortinet NSE 7 exam. NSE 7 certification is valid for two years from the date of completion. you will learn how FortiGate, FortiAP, FortiSwitch, and FortiAuthenticator enable secure connectivity over wired and wireless networks. You will also learn how to provision, administer, and monitor FortiAP and FortiSwitch devices using FortiManager. This course covers the deployment, integration, and troubleshooting of advanced authentication scenarios, as well as best practices for securely connecting wireless and wired users. You will learn how to keep the network secure by leveraging Fortinet Security Fabric integration between FortiGate, FortiSwitch, FortiAP, and FortiAnalyzer to automatically quarantine risky and compromised devices using IOC triggers.
NEW QUESTION 11
What is the diagnose test application ipsmonitor 99 command used for?
- A. To restart all IPS engines and monitors
- B. To provide information regarding IPS sessions
- C. To disable the IPS engine
- D. To enable IPS bypass mode
Answer: A
NEW QUESTION 12
Examine the output of the 'get router info ospfneighbor' command shown in the exhibit; then answer the question below.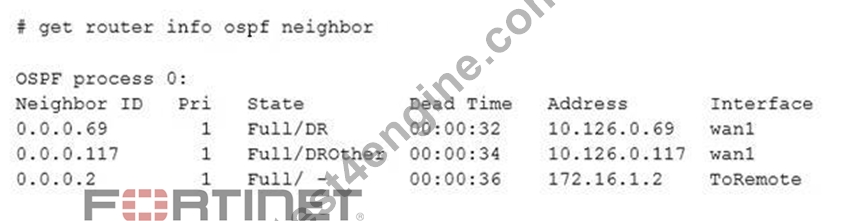
Which statements are true regarding the output in the exhibit? (Choose two.)
- A. The OSPF routers with the IDs 0.0.0.69 and 0.0.0.117 are both designated routers for the wan1 network.
- B. The OSPF router with the ID 0.0.0.2is the designated router for the ToRemote network.
- C. The interface ToRemote is OSPF network type point-to-point.
- D. The local FortiGate is the backup designated router for the wan1 network.
Answer: C,D
Explanation:
Explanation
https://www.cisco.com/c/en/us/support/docs/ip/open-shortest-path-first-ospf/13685-13.html
NEW QUESTION 13
What global configuration setting changes the behavior for content-inspected traffic while FortiGate is in system conserve mode?
- A. mem-failopen
- B. av-failopen
- C. ips-failopen
- D. utm-failopen
Answer: B
Explanation:
Explanation
https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-security-profiles-54/Other_Profile_Consideration
NEW QUESTION 14
View the exhibit, which contains the output of a debug command, and then answer the question below.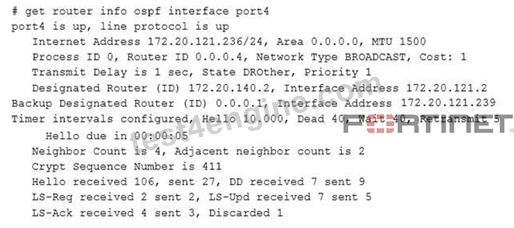
Which of the following statements about theexhibit are true? (Choose two.)
- A. In the network on port4, two OSPF routers are down.
- B. The local FortiGate's OSPF router ID is 0.0.0.4
- C. Port4 is connected to the OSPF backbone area.
- D. The local FortiGate has been elected as the OSPF backup designated router.
Answer: B,C
NEW QUESTION 15
Refer to the exhibit, which contains the partial output of a diagnose command.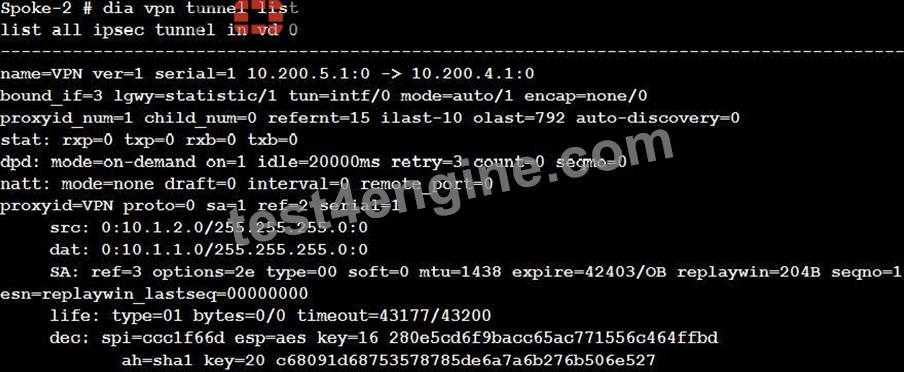
Based on the output, which two statements arecorrect? (Choose two.)
- A. Quick mode selectors are disabled.
- B. Remote gateway IP is 10.200.4.1.
- C. Anti-replay is enabled.
- D. DPD is disabled.
Answer: B,C
NEW QUESTION 16
View the exhibit, which contains the output of a BGP debug command, and then answer the question below.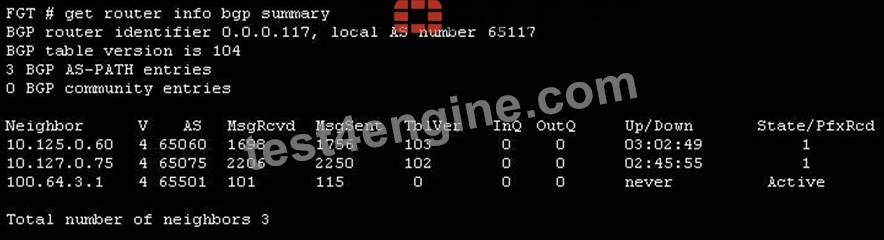
Which ofthe following statements about the exhibit are true? (Choose two.)
- A. The local router has received atotal of three BGP prefixes from all peers.
- B. Since the counters were last reset; the 10.200.3.1 peer has never been down.
- C. The local router's BGP state is Established with the 10.125.0.60 peer.
- D. The local router has not established a TCP session with 100.64.3.1.
Answer: C,D
NEW QUESTION 17
An administrator has enabled HA session synchronization in a HA cluster with two members. Which flag is added to a primary unit's session to indicate that it has been synchronized to the secondary unit?
- A. synced
- B. dirty.
- C. nds.
- D. redir.
Answer: A
Explanation:
Explanation
The synced sessions have the 'synced' flag. The command 'diag sys session list' can be used to see the sessions on the member, with the associated flags.
NEW QUESTION 18
An administrator cannot connect to the GIU of a FortiGate unit with the IP address 10.0.1.254. The administrator runs thedebug flow while attempting the connection using HTTP. The output of the debug flow is shown in the exhibit: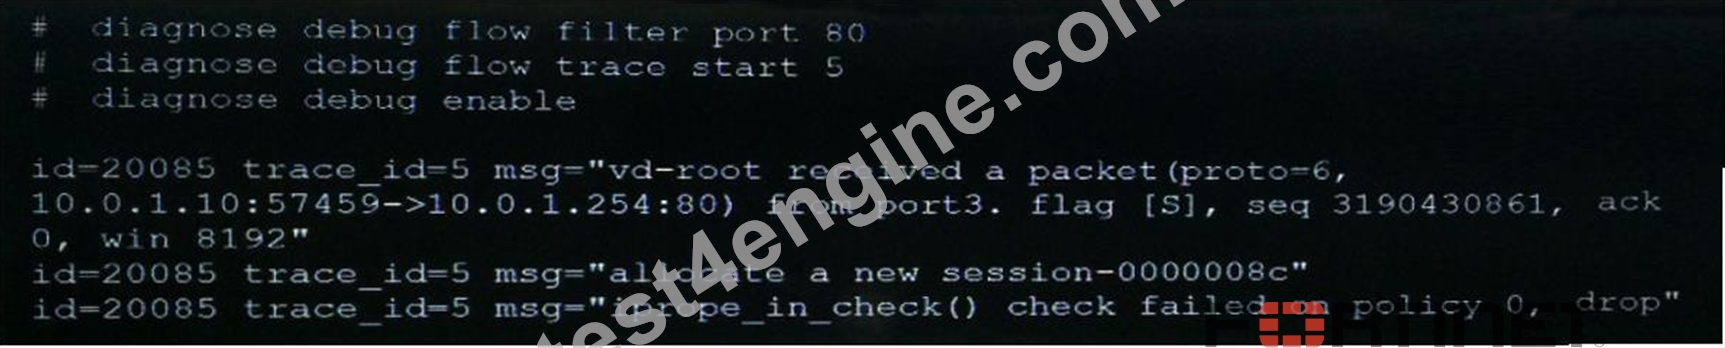
Based on the error displayed by the debug flow, which are valid reasons for this problem? (Choose two.)
- A. Redirection of HTTP to HTTPS administrative access is disabled.
- B. HTTP administrative access is disabled in the FortiGate interface with the IP address 10.0.1.254.
- C. HTTP administrative access is configured with a port number different than 80.
- D. The packet is denied because of reverse path forwarding check.
Answer: B,C
NEW QUESTION 19
What does the dirty flag mean in aFortiGate session?
- A. The next packet must be re-evaluated against the firewall policies.
- B. Traffic has been identified as from an application that is not allowed.
- C. The session must be removed from the former primary unit after an HA failover.
- D. Traffic has been blocked by the antivirus inspection.
Answer: A
Explanation:
Explanation
https://kb.fortinet.com/kb/viewContent.do?externalId=FD40119&sliceId=1
NEW QUESTION 20
Examine the output of the 'diagnose ips anomaly list' command shown in the exhibit; then answer the question below.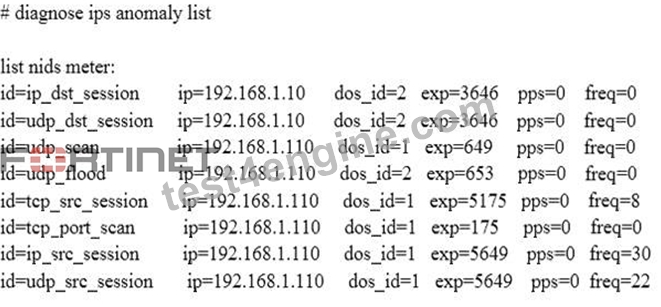
Which IP addresses are included in the output of thiscommand?
- A. Those whose traffic matches an IPS sensor.
- B. Those whose traffic exceeded a threshold of a matching DoS policy.
- C. Those whose traffic was detected as an anomaly by an IPS sensor.
- D. Those whose traffic matches a DoS policy.
Answer: D
NEW QUESTION 21
A FortiGate has two default routes: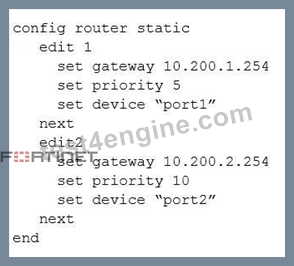
All Internet traffic is currently using port1. The exhibit shows partial information for one sample session of Internet traffic from an internal user: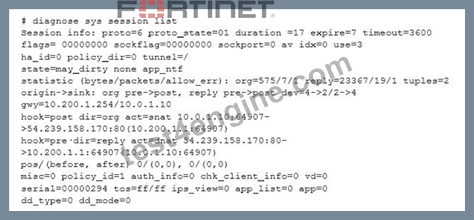
What would happen with the traffic matching the above session if the priority on the firstdefault route (IDd1) were changed from 5 to 20?
- A. Session would remain in the session table and its traffic would start using port2 as the outgoing interface.
- B. Session would be deleted, so the client would need to start a new session.
- C. Session would remain in the session table and its traffic would be shared between port1 and port2.
- D. Session would remain in the session table and its traffic would keep using port1 as the outgoing interface.
Answer: D
NEW QUESTION 22
View the exhibit, which contains the output of a debug command, and then answer the question below.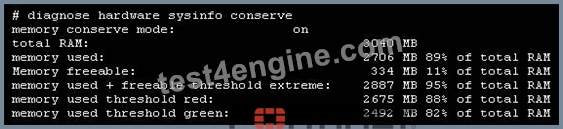
Which one of the following statements about this FortiGate is correct?
- A. It is currently in system conserve mode because of high CPU usage.
- B. It is currently in extreme conserve mode because of high memory usage.
- C. It is currently in proxy conserve mode because of high memory usage.
- D. It is currently in memory conserve mode because of high memory usage.
Answer: D
NEW QUESTION 23
Which two tasks are automated using the Install Wizard on FortiManager? (Choose two.)
- A. Preview pending configuration changes for managed devices.
- B. Import policy packages from managed devices.
- C. Install configuration changes to managed devices.
- D. Add devices to FortiManager.
- E. Import interface mappings from managed devices.
Answer: A,C
Explanation:
Explanation
https://help.fortinet.com/fmgr/50hlp/56/5-6-2/FortiManager_Admin_Guide/1000_Device%20Manager/1200_ins There are 4 main wizards:Add Device: is used to add devices to central management and import their configurations.
Install: is used to install configuration changes from Device Manager or Policies & Objects to the managed devices. It allows you to preview the changes and, if the administrator doesn't agree with the changes, cancel and modify them.
Import policy: is used to import interface mapping, policy database, and objects associated with the managed devices into a policy package under the Policy & Object tab. It runs with the Add Device wizard by default and may be run at any time from the managed device list.
Re-install policy: is used to perform a quick install of the policy package. It doesn't give the ability to preview the changes that will be installed to the managed device.
NEW QUESTION 24
What is the purpose of an internal segmentation firewall (ISFW)?
- A. It is anall-in-one security appliance that is placed at remote sites to extend the enterprise network.
- B. It splits the network into multiple security segments to minimize the impact of breaches.
- C. It is the first line of defense at the network perimeter.
- D. It inspects incoming traffic to protect services in the corporate DMZ.
Answer: B
Explanation:
Explanation
ISFW splits your network into multiple security segments. They serve as a breach containers from attacks that come from inside.
NEW QUESTION 25
View the exhibit, which contains a screenshot of some phase-1settings, and then answer the question below.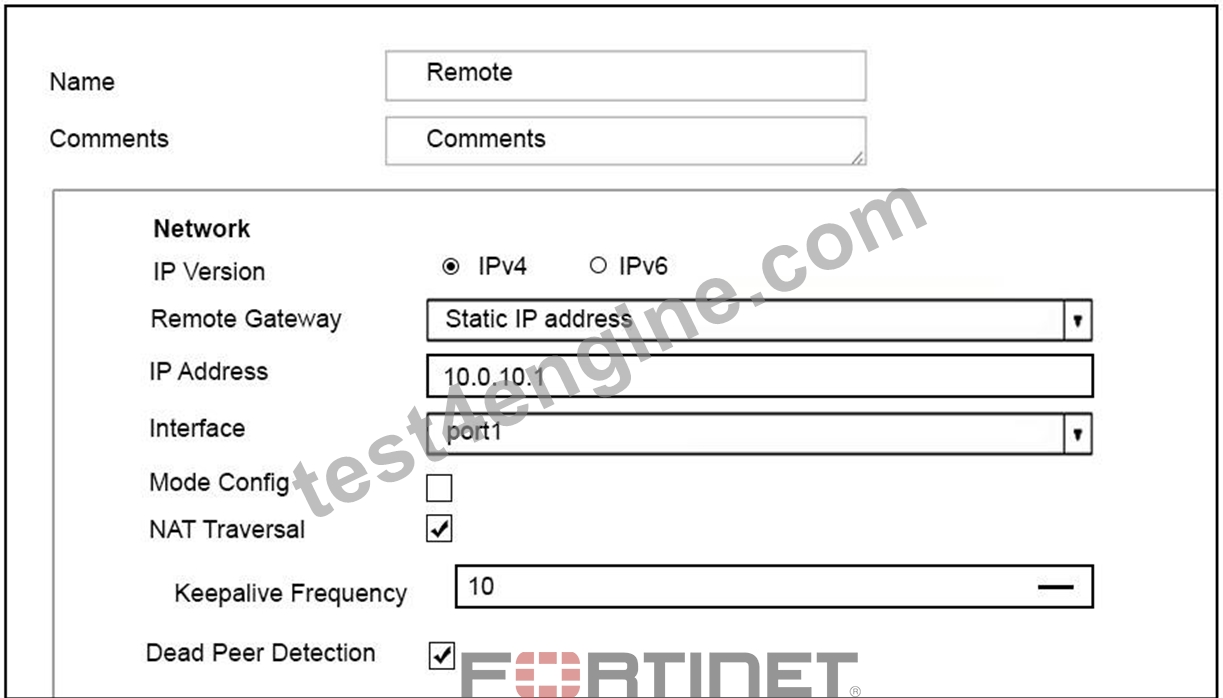
The VPN is up, and DPD packets are being exchanged between both IPsec gateways; however, traffic cannot pass through the tunnel. To diagnose, the administrator enters these CLI commands: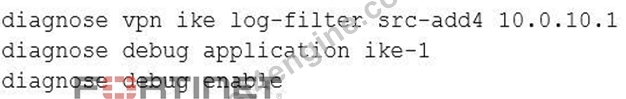
However, the IKE real time debug does not show any output. Why?
- A. The debug output shows phases 1 and 2 negotiations only. Once the tunnel is up, it does not show any more output.
- B. The debug output shows phase 1 negotiation only. After that, the administrator must enable the following real time debug: diagnose debug application ipsec -1.
- C. The log-filter setting was set incorrectly. The VPN's traffic does not match thisfilter.
- D. The debug shows only error messages. If there is no output, then the tunnel is operating normally.
Answer: C
NEW QUESTION 26
Examine the following traffic log; then answer the question below.
date-20xx-02-01 time=19:52:01 devname=master device_id="xxxxxxx" log_id=0100020007 type=event subtype=system pri critical vd=root service=kemel status=failure msg="NAT port is exhausted." What does the log mean?
- A. The limit for the maximum number of entries in the NAT port table has been reached.
- B. The limit for the maximum number of simultaneous sessions sharing the same NAT port has been reached.
- C. FortiGate does not have any available NAT port for a new connection.
- D. There is not enough available memory in the system to create a new entry inthe NAT port table.
Answer: B
NEW QUESTION 27
View the exhibit, which contains theoutput of get sys ha status, and then answer the question below.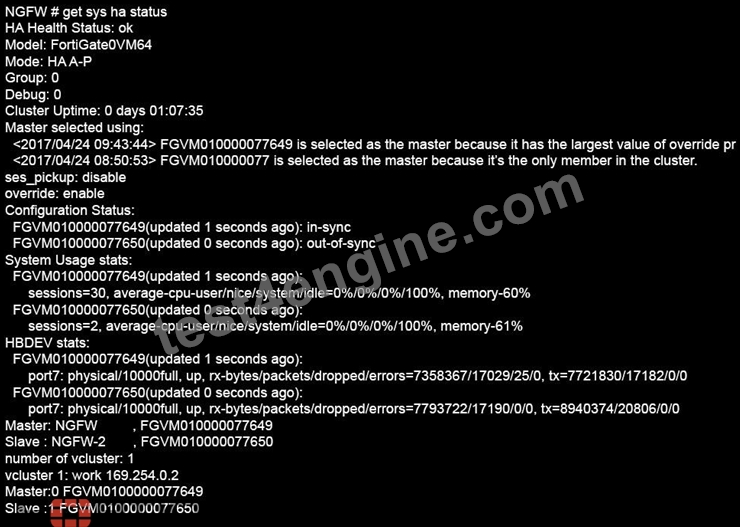
Which statements are correct regarding the output? (Choose two.)
- A. The slave configuration is not synchronized with the master.
- B. port 7 is used the HA heartbeat on all devices in the cluster.
- C. The HA management IP is 169.254.0.2.
- D. Master is selected because it is the only device in the cluster.
Answer: A,B
NEW QUESTION 28
Examine the IPsec configuration shown in the exhibit; then answer the question below.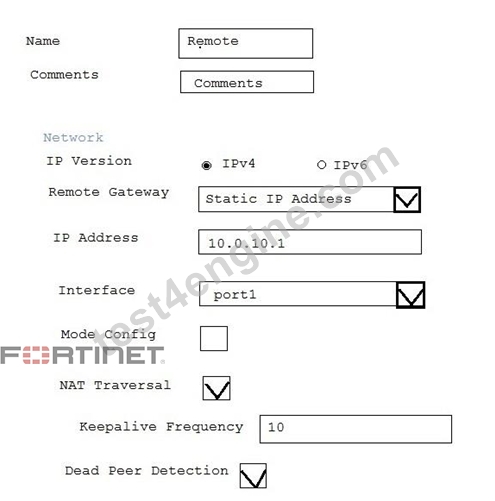
An administrator wants to monitor the VPN by enabling theIKE real time debug using these commands:
diagnose vpn ike log-filter src-addr4 10.0.10.1
diagnose debug application ike -1
diagnose debug enable
The VPN is currently up, there is no traffic crossing the tunnel and DPD packets are beinginterchanged between both IPsec gateways. However, the IKE real time debug does NOT show any output. Why isn't there any output?
- A. The IKE real time debug shows the phase 1 negotiation only. For information after that, the administrator must use the IPsec real time debug instead: diagnose debug application ipsec -1.
- B. The log-filter setting is set incorrectly. The VPN's traffic does not match this filter.
- C. The IKE real time debug shows error messages only. If it does not provide any output, it indicates that the tunnel is operating normally.
- D. The IKE real time shows the phases 1 and 2 negotiations only. It does not show any more output once the tunnel is up.
Answer: B
NEW QUESTION 29
Which statements about bulk configuration changes using FortiManager CLI scripts are correct? (Choose two.)
- A. When executed on the All FortiGate in ADOM, changes are automatically installed without creating a new revision history.
- B. When executed on the Remote FortiGate directly, administrators do not have the option to review the changes prior to installation.
- C. When executed on the Device Database, you must use the installation wizard to apply the changes to the managed FortiGate.
- D. When executed on the Policy Package, ADOM database, changes are applied directly to the managed FortiGate.
Answer: B,C
Explanation:
Explanation
CLI scripts can be run in three different ways:Device Database: By default, a script is executed on the device database. It is recommend you run the changes on the device database (default setting), as this allows you to check what configuration changes you will send to the managed device. Once scripts are run on the device database, you can install these changes to a managed device using the installation wizard.
Policy Package, ADOM database: If a script contains changes related to ADOM level objects and policies, you can change the default selection to run on Policy Package, ADOM database and can then be installed using the installation wizard.
Remote FortiGate directly (through CLI): A script can be executed directly on the device and you don't need to install these changes using the installation wizard. As the changes are directly installed on the managed device, no option is provided to verify and check the configuration changes through FortiManager prior to executing it.
NEW QUESTION 30
Examine thefollowing partial outputs from two routing debug commands; then answer the question below: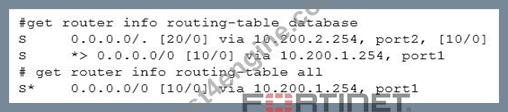
Why the default route using port2 is not displayed in the output of the second command?
- A. It hasa higher priority than the default route using port1.
- B. It is disabled in the FortiGate configuration.
- C. It has a higher distance than the default route using port1.
- D. It has a lower priority than the default route using port1.
Answer: C
Explanation:
Explanation
http://kb.fortinet.com/kb/viewContent.do?externalId=FD32103
NEW QUESTION 31
Examine the output of the 'get router info ospf interface' command shown in the exhibit; then answer the question below.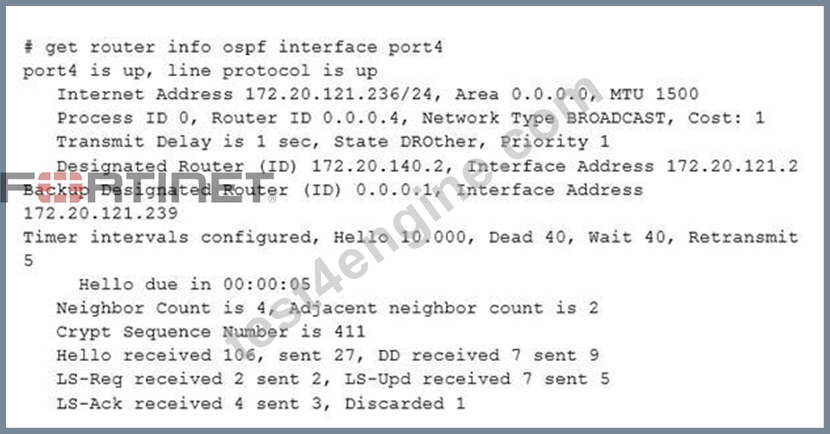
Which statements are true regarding the above output? (Choose two.)
- A. Two OSPF routers are down in the port4 network.
- B. Theport4 interface is connected to the OSPF backbone area.
- C. There are at least 5 OSPF routers connected to the port4 network.
- D. The local FortiGate has been elected as the OSPF backup designated router.
Answer: B,C
Explanation:
Explanation
on BROADCAST network there are 4 neighbors, among which 1*DR +1*BDR. So our FG has 4 neighbors, but create adjacency only with 2 (with DR and BDR). 2 neighbors DRother (not down).
NEW QUESTION 32
When using the SSL certificate inspection method to inspect HTTPS traffic, how does FortiGate filter web requests when the client browser does notprovide the server name indication (SNI) extension?
- A. FortiGate uses the CN information from the Subject field in the server certificate.
- B. FortiGate blocks the request without any furtherinspection.
- C. FortiGate switches to the full SSL inspection method to decrypt the data.
- D. FortiGate uses the requested URL from the user's web browser.
Answer: A
NEW QUESTION 33
View the exhibit, which contains the partial output of an IKE real-time debug, and then answer the question below.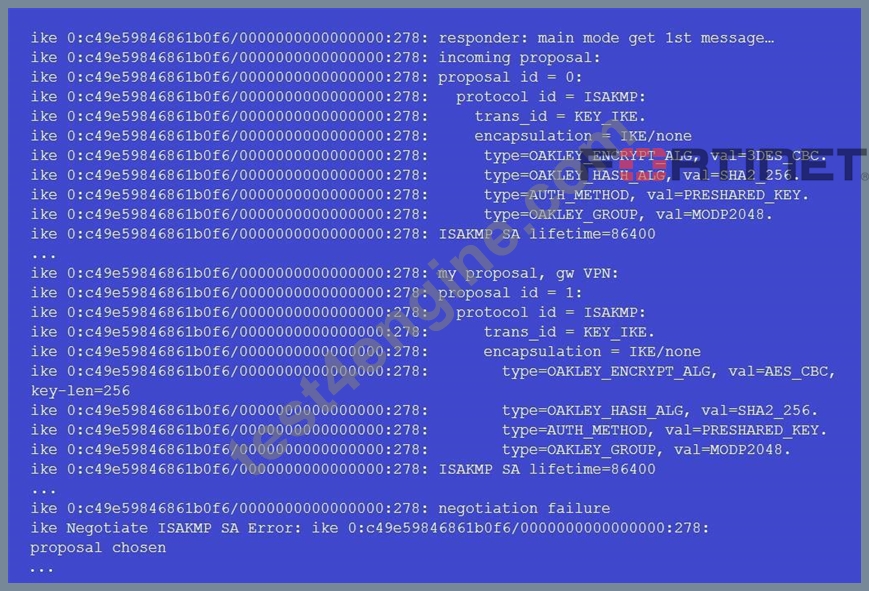
Why didn't the tunnel come up?
- A. The remote gateway's phase 2configuration does not match the local gateway's phase 2 configuration.
- B. The pre-shared keys do not match.
- C. The remote gateway is using aggressive mode and the local gateway is configured to use man mode.
- D. The remote gateway's phase 1 configuration does not match the local gateway's phase 1 configuration.
Answer: D
NEW QUESTION 34
......
Ultimate Guide to Prepare NSE7_EFW-6.4 Certification Exam for NSE 7 Network Security Architect: https://www.test4engine.com/NSE7_EFW-6.4_exam-latest-braindumps.html
NSE7_EFW-6.4 Ultimate Study Guide: https://drive.google.com/open?id=1bKpN9ZUd4qBw_ONi31s4jGUmkjurHPgB