


Get ready to pass the SPLK-1003 Exam right now using our Splunk Enterprise Certified Admin Exam Package
A fully updated 2021 SPLK-1003 Exam Dumps exam guide from training expert Test4Engine
NEW QUESTION 13
Which of the following statements accurately describes using SSL to secure the feed from a forwarder?
- A. It does not encrypt the certificate password.
- B. It requires that the receiver be set to compression=true.
- C. It requires that the forwarder be set to compressed=true.
- D. SSL automatically compresses the feed by default.
Answer: A
NEW QUESTION 14
When configuring monitor inputs with whitelists or blacklists, what is the supported method of filtering the lists?
- A. Irregular expression
- B. Slash notation
- C. Regular expression
- D. Wildcard-only expression
Answer: D
NEW QUESTION 15
Local user accounts created in Splunk store passwords in which file?
- A. $SPLUNK_HOME/etc/passwd
- B. $SPLUNK_HOME/etc/users/passwd.conf
- C. $SPLUNK_HOME/etc/users/authentication.conf
- D. $SPLUNK_HOME/etc/authentication
Answer: A
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Admin/User-seedconf
NEW QUESTION 16
The Splunk administrator wants to ensure data is distributed evenly amongst the indexers. To do this, he runs the following search over the last 24 hours:
index=*
What field can the administrator check to see the data distribution?
- A. splunk_server
- B. host
- C. index
- D. linecount
Answer: A
NEW QUESTION 17
Which configuration file would be used to forward the Splunk internal logs from a search head to the indexer?
- A. collections.conf
- B. outputs.conf
- C. inputs.conf
- D. props.conf
Answer: B
NEW QUESTION 18
If an update is made to an attribute in inputs.confon a universal forwarder, on which Splunk component would the fishbucket need to be reset in order to reindex the data?
- A. Deployment server
- B. Indexer
- C. Forwarder
- D. Search head
Answer: B
Explanation:
Explanation/Reference:
Reference https://community.splunk.com/t5/Archive/How-to-reindex-data-from-a-forwarder/td-p/93310
NEW QUESTION 19
What is the valid option for a [monitor] stanza in inputs.conf?
- A. server_name
- B. datasource
- C. enabled
- D. ignoreOlderThan
Answer: D
NEW QUESTION 20
In this source definition the MAX_TIMESTAMP_LOOKHEAD is missing. Which value would fit best?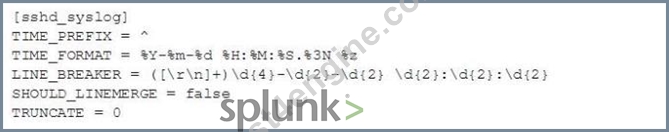
Event example:
- A. MAX TIMESTAMP LOOKAHEAD - 30
- B. MAX_TIMESTAMF_LOOKHEAD = 20
- C. MAX_TIMESTAMP_LOOKAHEAD - 10
- D. MAX_TIMESTAMP_L0CKAHEAD = 5
Answer: A
NEW QUESTION 21
You update a props.conffile while Splunk is running. You do not restart Splunk and you run this command:
splunk btool props list --debug. What will the output be?
- A. A list of props.confconfigurations as they are on-disk along with a file path from which the configuration is located.
- B. A list of all the configurations on-disk that Splunk contains.
- C. A verbose list of all configurations as they were when splunkd started.
- D. A list of the current running props.confconfigurations along with a file path from which the configuration was made.
Answer: D
Explanation:
Explanation/Reference: https://answers.splunk.com/answers/494219/need-help-with-what-should-be-a-simple- precedence.html
NEW QUESTION 22
Where are license files stored?
- A. $SPLUNK_HOME/etc/secure
- B. $SPLUNK_HOME/etc/licenses
- C. $SPLUNK_HOME/etc/apps/licenses
- D. $SPLUNK_HOME/etc/system
Answer: B
NEW QUESTION 23
Which of the following is valid distribute search group?
A)
B)
C)
D)
- A. option A
- B. Option D
- C. Option B
- D. Option C
Answer: B
NEW QUESTION 24
Which of the following statements accurately describes using SSL to secure the feed from a forwarder?
- A. It does not encrypt the certificate password.
- B. It requires that the receiver be set to compression=true.
- C. It requires that the forwarder be set to compressed=true.
- D. SSL automatically compresses the feed by default.
Answer: A
Explanation:
Reference:
AboutsecuringyourSplunkconfigurationwithSSL
NEW QUESTION 25
Which of the following statements describe deployment management? (Choose all that apply.)
- A. Can automatically restart the host OS running the forwarder.
- B. Requires an Enterprise license.
- C. Once used, is the only way to manage forwarders.
- D. Is responsible for sending apps to forwarders.
Answer: B
NEW QUESTION 26
Which layers are involved in Splunk configuration file layering? (select all that apply)
- A. App context
- B. User context
- C. Forwarder context
- D. Global context
Answer: A,B
NEW QUESTION 27
Social Security Numbers (PII) data is found in log events, which is against company policy. SSN format is as follows: 123-44-5678.
Which configuration file and stanza pair will mask possible SSNs in the log events?
- A. transforms.conf
[mask-SSN]
REGEX = (?ms)^(.)\<[SSN>\d{3}-?\d{2}-?(\d{4}.*)$"
FORMAT = $1<SSN>###-##-$2
DEST_KEY = _raw - B. transforms.conf
[mask-SSN]
REX = (?ms)^(.)\<[SSN>\d{3}-?\d{2}-?(\d{4}.*)$"
FORMAT = $1<SSN>###-##-$2
DEST_KEY = _raw - C. props.conf
[mask-SSN]
REX = (?ms)^(.)\<[SSN>\d{3}-?\d{2}-?(\d{4}.*)$"
FORMAT = $1<SSN>###-##-$2
KEY = _raw - D. props.conf
[mask-SSN]
REGEX = (?ms)^(.)\<[SSN>\d{3}-?\d{2}-?(\d{4}.*)$"
FORMAT = $1<SSN>###-##-$2
DEST_KEY = _raw
Answer: D
NEW QUESTION 28
Which option accurately describes the purpose of the HTTP Event Collector (HEC)?
- A. A token-based HTTP input that is secure and scalable and that does not require the use of forwarders.
- B. A token-based HTTP input that is secure and scalable and that requires the use of forwarders
- C. A token-based HTTP input that is insecure and non-scalable and that does not require the use of forwarders.
- D. An agent-based HTTP input that is secure and scalable and that does not require the use of forwarders.
Answer: B
NEW QUESTION 29
With authentication methods are natively supported within Splunk Enterprise? (Select all that apply.)
- A. LDAP
- B. SAML
- C. RADIUS
- D. Duo Multifactor Authentication
Answer: A,D
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Security/SetupuserauthenticationwithSplunk
NEW QUESTION 30
What type of data is counted against the Enterprise license at a fixed 150 bytes per event?
- A. Internal Splunk data
- B. Metricsdata
- C. Internal Windows logs
- D. License data
Answer: B
NEW QUESTION 31
......
Master 2021 Latest The Questions Splunk Enterprise Certified Admin and Pass SPLK-1003 Real Exam!: https://www.test4engine.com/SPLK-1003_exam-latest-braindumps.html
Practice To SPLK-1003 - Test4Engine Remarkable Practice On your Splunk Enterprise Certified Admin Exam: https://drive.google.com/open?id=10haSBq_AS1bebWRNkHBDz_lszE0WyQ2C