


Splunk Enterprise Certified Admin SPLK-1003 Dumps | Updated Jul 06, 2023 - Test4Engine
Master 2023 Latest The Questions Splunk Enterprise Certified Admin and Pass SPLK-1003 Real Exam!
NEW QUESTION # 19
Which option on the Add Data menu is most useful for testing data ingestion without creating inputs.conf?
- A. Forward option
- B. Download option
- C. Upload option
- D. Monitor option
Answer: C
NEW QUESTION # 20
To set up a Network input in Splunk, what needs to be specified'?
- A. Network protocol and MAC address.
- B. Network protocol and port number.
- C. File path.
- D. Username and password
Answer: B
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.0.3/Data/Monitornetworkports
NEW QUESTION # 21
Which Splunk indexer operating system platform is supported when sending logs from a Windows universal forwarder?
- A. Linux platform only.
- B. None of the above.
- C. Windows platform only.
- D. Any OS platform.
Answer: B
Explanation:
Explanation/Reference:
https://docs.splunk.com/Documentation/Splunk/7.3.2/Installation/Systemrequirements#Supported_OSes
NEW QUESTION # 22
On the deployment server, administrators can map clients to server classes using client filters. Which of the following statements is accurate?
- A. Machine type filters are applied before the whitelist and blacklist.
- B. The whitelist takes precedence over the blacklist.
- C. The blacklist takes precedence over the whitelist.
- D. Wildcards are not supported in any client filters.
Answer: C
Explanation:
Explanation/Reference: https://community.splunk.com/t5/Getting-Data-In/Can-I-use-both-the-whitelist-AND-blacklist-for-the- same/td-p/390910
NEW QUESTION # 23
Which is a valid stanza for a network input?
[udp://172.16.10.1:9997]
- A. connection_host = dns
sourcetype = dns - B. connection = dns
sourcetype = dns
[any://172.16.10.1:10001] - C. connection_host = web
sourcetype = web
[tcp://172.16.10.1:10001] - D. connection_host = ip
sourcetype = web
[tcp://172.16.10.1:9997]
Answer: C
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/SplunkCloud/8.0.2006/Data/ Bypassautomaticsourcetypeassignment
NEW QUESTION # 24
When indexing a data source, which fields are considered metadata?
- A. source, host, time
- B. time, sourcetype, source
- C. host, raw, sourcetype
- D. sourcetype, source, host
Answer: D
NEW QUESTION # 25
An admin is running the latest version of Splunk with a 500 GB license. The current daily volume of new data is 300 GB per day. To minimize license issues, what is the best way to add 10 TB of historical data to the index?
- A. Add 2.5 TB each day for the next 5 days.
- B. Add 200 GB of historical data each day for 50 days.
- C. Add all 10 TB in a single 24 hour period.
- D. Buy a bigger Splunk license.
Answer: C
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.1.2/Admin/Aboutlicenseviolations
"An Enterprise license stack with a license volume of 100 GB of data per day or more does not currently violate."
NEW QUESTION # 26
Which of the following is valid distribute search group?
A)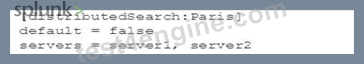
B)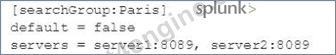
C)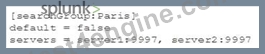
D)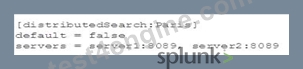
- A. Option D
- B. Option C
- C. Option B
- D. option A
Answer: A
NEW QUESTION # 27
Where can scripts for scripted inputs reside on the host file system? (select all that apply)
- A. $SFLUNK_HOME/bin/scripts
- B. $SPLUNK_HOME/etc/system/bin
- C. $SPLUNK_HOME/etc/apps/bin
- D. $S?LUNK_HOME/etc/apps/<your_app>/bin_
Answer: B
NEW QUESTION # 28
Which of the following monitor inputs stanza headers would match all of the following files?
/var/log/www1/secure.log
/var/log/www/secure.l
/var/log/www/logs/secure.logs
/var/log/www2/secure.log
- A. [monitor:///var/log/www*/secure.*]
- B. [monitor:///var/log/www1/secure.*]
- C. [monitor:///var/log/.../secure.*
- D. [monitor:///var/log/www1/secure.log]
Answer: D
NEW QUESTION # 29
Which Splunk component does a search head primarily communicate with?
- A. Deployment server
- B. Cluster master
- C. Forwarder
- D. Indexer
Answer: D
NEW QUESTION # 30
Which of the following are required when defining an index in indexes. conf? (select all that apply)
- A. thawedPath
- B. homePath
- C. frozenPath
- D. coldPath
Answer: B
NEW QUESTION # 31
Which Splunk indexer operating system platform is supported when sending logs from a Windows universal forwarder?
- A. Linux platform only
- B. None of the above.
- C. Windows platform only.
- D. Any OS platform
Answer: C
NEW QUESTION # 32
Within props. conf, which stanzas are valid for data modification? (select all that apply)
- A. Server
- B. Source
- C. Host
- D. Sourcetype
Answer: B,C,D
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.0.4/Admin/Propsconf#props.conf.spec
https://docs.splunk.com/Documentation/Splunk/8.1.1/Admin/Propsconf
"* Reuse of the same field-extracting regular expression across multiple sources, source types, or hosts." https://docs.splunk.com/Documentation/Splunk/8.0.4/Admin/Propsconf#props.conf.spec
NEW QUESTION # 33
In which Splunk configuration is the SEDCMDused?
- A. indexes.conf
- B. transforms.conf
- C. props.conf
- D. inputs.conf
Answer: C
Explanation:
Explanation
Explanation/Reference: https://answers.splunk.com/answers/212128/why-sedcmd-configured-in-propsconf-is-working- duri.html
NEW QUESTION # 34
In which Splunk configuration is the SEDCMD used?
- A. indexes.conf
- B. transforms.conf
- C. props, conf
- D. inputs.conf
Answer: C
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.0.5/Forwarding/Forwarddatatothird-partysystemsd
"You can specify a SEDCMD configuration in props.conf to address data that contains characters that the third-party server cannot process. "
NEW QUESTION # 35
The universal forwarder has which capabilities when sending data? (select all that apply)
- A. Compressing data
- B. Sending alerts
- C. Obfuscating/hiding data
- D. Indexer acknowledgement
Answer: A,D
Explanation:
Explanation
https://docs.splunk.com/Documentation/Splunk/8.0.1/Forwarding/Aboutforwardingandreceivingdata
NEW QUESTION # 36
Which of the following must be done to define user permissions when integrating Splunk with LDAP?
- A. Map LDAP to Active Directory
- B. Map Groups
- C. Map LDAP Inheritance
- D. Map Users
Answer: B
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.1.3/Security/ConfigureLDAPwithSplunkWeb
"You can map either users or groups, but not both. If you are using groups, all users must be members of an appropriate group. Groups inherit capabilities form the highest level role they're a member of." "If your LDAP environment does not have group entries, you can treat each user as its own group."
NEW QUESTION # 37
What is the valid option for a [monitor] stanza in inputs.conf?
- A. server_name
- B. enabled
- C. datasource
- D. ignoreOlderThan
Answer: D
Explanation:
Reference:
Monitorfilesanddirectorieswithinputs.conf
NEW QUESTION # 38
When running a real-time search, search results are pulled from which Splunk component?
- A. Heavy forwarders and search peers
- B. Search peers
- C. Search heads
- D. Heavy forwarders
Answer: C
NEW QUESTION # 39
On the deployment server, administrators can map clients to server classes using client filters. Which of the following statements is accurate?
- A. Machine type filters are applied before the whitelist and blacklist.
- B. The whitelist takes precedence over the blacklist.
- C. The blacklist takes precedence over the whitelist.
- D. Wildcards are not supported in any client filters.
Answer: C
Explanation:
Reference:
same/td-p/390910
NEW QUESTION # 40
Which additional component is required for a search head cluster?
- A. Cluster Master
- B. Management Console
- C. Deployer
- D. Monitoring Console
Answer: C
Explanation:
Reference:
The deployer. This is a Splunk Enterprise instance that distributes apps and other configurations to the cluster members. It stands outside the cluster and cannot run on the same instance as a cluster member. It can, however, under some circumstances, reside on the same instance as other Splunk Enterprise components, such as a deployment server or an indexer cluster master node.
NEW QUESTION # 41
......
A fully updated 2023 SPLK-1003 Exam Dumps exam guide from training expert Test4Engine: https://www.test4engine.com/SPLK-1003_exam-latest-braindumps.html
Practice To SPLK-1003 - Test4Engine Remarkable Practice On your Splunk Enterprise Certified Admin Exam: https://drive.google.com/open?id=1JmAB9Xde0HvWKUjPYz0Y64b2pytX2PVV