


[Jul 07, 2023] Get Free Updates Up to 365 days On Developing SPLK-1003 Braindumps
Best Quality Splunk SPLK-1003 Exam Questions
NEW QUESTION # 56
Which option on the Add Data menu is most useful for testing data ingestion without creating inputs.conf?
- A. Monitor option
- B. Upload option
- C. Download option
- D. Forward option
Answer: A
NEW QUESTION # 57
What is the valid option for a [monitor] stanza in inputs.conf?
- A. datasource
- B. ignoreOlderThan
- C. server_name
- D. enabled
Answer: B
Explanation:
Setting: ignoreOlderThan = <time_window> Description: "Causes the input to stop checking files for updates if the file modification time has passed the <time_window> threshold." Default: 0 (disabled) Reference:
Monitorfilesanddirectorieswithinputs.conf
NEW QUESTION # 58
How is a remote monitor input distributed to forwarders?
- A. As a forwarder monitor profile.
- B. As an app.
- C. As a monitor.conf file.
- D. As a forward.conf file.
Answer: B
NEW QUESTION # 59
After configuring a universal forwarder to communicate with an indexer, which index can be checked via the Splunk Web UI for a successful connection?
index=main
- A. index=test
- B. index=_internal
- C. index=summary
Answer: B
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/8.0.5/Security/Validateyourconfiguration
NEW QUESTION # 60
Which of the following enables compression for universal forwarders in outputs. conf ?
A)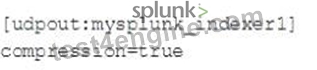
B)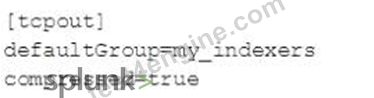
C)
D)
- A. Option A
- B. Option B
- C. Option D
- D. Option C
Answer: B
NEW QUESTION # 61
User role inheritance allows what to be inherited from the parent role? (select all that apply)
- A. Search history
- B. Capabilities
- C. Parents
- D. Index access
Answer: B,D
Explanation:
https://docs.splunk.com/Documentation/Splunk/latest/Security/Aboutusersandroles#Role_inheritance
https://docs.splunk.com/Documentation/Splunk/7.3.1/Security/Aboutusersandroles#How_users_inherit_capabilities
NEW QUESTION # 62
If an update is made to an attribute in inputs.conf on a universal forwarder, on which Splunk component would the fishbucket need to be reset in order to reindex the data?
- A. Forwarder
- B. Search head
- C. Deployment server
- D. Indexer
Answer: D
Explanation:
Reference https://community.splunk.com/t5/Archive/How-to-reindex-data-from-a-forwarder/td-p/93310
NEW QUESTION # 63
Which Splunk component consolidates the individual results and prepares reports in a distributed environment?
- A. Forwarder
- B. Search head
- C. Indexers
- D. Search peers
Answer: C
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Indexer/Advancedindexingstrategy
NEW QUESTION # 64
Which of the following are required when defining an index in indexes. conf? (select all that apply)
- A. homePath
- B. thawedPath
- C. coldPath
- D. frozenPath
Answer: A,B,C
NEW QUESTION # 65
You update a props. conf file while Splunk is running. You do not restart Splunk and you run this command: splunk btoo1 props list -debug. What will the output be?
- A. A list of the current running props, conf configurations along with a file path from which the configuration was made
- B. list of all the configurations on-disk that Splunk contains.
- C. A list of props. conf configurations as they are on-disk along with a file path from which the configuration is located
- D. A verbose list of all configurations as they were when splunkd started.
Answer: C
NEW QUESTION # 66
What is the correct order of steps in Duo Multifactor Authentication?
- A. 1. Request Login 2 Duo MFA
3. Authentication Granted 4 Connect to SAML server
5. Log into Splunk
6. Create User session - B. 1 Request Login
2 Check authentication / group mapping
3 Authentication Granted
4. Duo MFA
5. Create User session
6. Log into Splunk - C. 1 Request Login
2. Connect to SAML server
3 Duo MFA
4 Create User session
5 Authentication Granted 6. Log into Splunk - D. 1 Request Login 2 Duo MFA
3. Check authentication / group mapping
4 Create User session
5. Authentication Granted
6 Log into Splunk
Answer: D
NEW QUESTION # 67
What is the correct order of steps in Duo Multifactor Authentication?
- A. 1 Request Login 2 Duo MFA
3. Check authentication / group mapping
4 Create User session
5. Authentication Granted
6 Log into Splunk - B. 1. Request Login 2 Duo MFA
3. Authentication Granted 4 Connect to SAML server
5. Log into Splunk
6. Create User session - C. 1 Request Login
2. Connect to SAML server
3 Duo MFA
4 Create User session
5 Authentication Granted 6. Log into Splunk - D. 1 Request Login
2 Check authentication / group mapping
3 Authentication Granted
4. Duo MFA
5. Create User session
6. Log into Splunk
Answer: D
NEW QUESTION # 68
Which Splunk indexer operating system platform is supported when sending logs from a Windows universal forwarder?
- A. None of the above.
- B. Any OS platform
- C. Windows platform only.
- D. Linux platform only
Answer: C
NEW QUESTION # 69
To set up a Network input in Splunk, what needs to be specified'?
- A. Network protocol and MAC address.
- B. Username and password
- C. Network protocol and port number.
- D. File path.
Answer: B
NEW QUESTION # 70
The CLI command splunk add forward-server indexer:<receiving-port> will create stanza(s) in which configuration file?
- A. servers.conf
- B. indexes.conf
- C. outputs.conf
- D. inputs.conf
Answer: C
Explanation:
The CLI command "Splunk add forward-server indexer:<receiving-port>" is used to define the indexer and the listening port on forwards. The command creates this kind of entry "[tcpout-server://<ip address>:<port>]" in the outputs.conf file.
https://docs.splunk.com/Documentation/Forwarder/8.2.2/Forwarder/Configureforwardingwithoutputs.conf
NEW QUESTION # 71
Which Splunk component requires a Forwarder license?
- A. Universal forwarder
- B. Search head
- C. Heaviest forwarder
- D. Heavy forwarder
Answer: D
Explanation:
Explanation/Reference: https://answers.splunk.com/answers/70017/heavy-forwarder-costs-and-licenses.html
NEW QUESTION # 72
Which of the following is valid distribute search group?
A)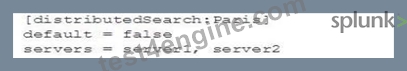
B)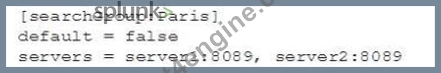
C)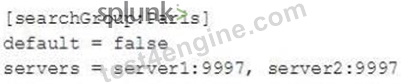
D)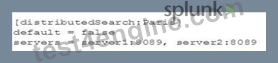
- A. option A
- B. Option B
- C. Option D
- D. Option C
Answer: C
NEW QUESTION # 73
Within props. conf, which stanzas are valid for data modification? (select all that apply)
- A. Host
- B. Source
- C. Sourcetype
- D. Server
Answer: A,B,C
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.0.4/Admin/Propsconf#props.conf.spec
https://docs.splunk.com/Documentation/Splunk/8.1.1/Admin/Propsconf
"* Reuse of the same field-extracting regular expression across multiple sources, source types, or hosts." https://docs.splunk.com/Documentation/Splunk/8.0.4/Admin/Propsconf#props.conf.spec
NEW QUESTION # 74
What options are available when creating custom roles? (select all that apply)
- A. Limit the number of concurrent search jobs
- B. Restrict search terms
- C. Whitelist search terms
- D. Allow or restrict indexes that can be searched.
Answer: A,B,D
Explanation:
https://docs.splunk.com/Documentation/SplunkCloud/8.2.2106/Admin/ConcurrentLimits
"Set limits for concurrent scheduled searches. You must have the edit_search_concurrency_all and edit_search_concurrency_scheduled capabilities to configure these settings."
NEW QUESTION # 75
Which feature in Splunk allows Event Breaking, Timestamp extractions, and any advanced configurations found in props.conf to be validated all through the UI?
- A. Forwarder inputs
- B. Data preview
- C. Search
- D. Apps
Answer: B
Explanation:
http://www.splunk.com/view/SP-CAAAGPR
NEW QUESTION # 76
Local user accounts created in Splunk store passwords in which file?
- A. $SPLUNK_HOME/etc/authentication
- B. $SPLUNK_HOME/etc/users/passwd.conf
- C. $SPLUNK_HOME/etc/users/authentication.conf
- D. $SPLUNK_HOME/etc/passwd
Answer: D
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Admin/User-seedconf
NEW QUESTION # 77
Which configuration files are used to transform raw data ingested by Splunk? (Choose all that apply.)
- A. rawdata.conf
- B. transforms.conf
- C. props.conf
- D. inputs.conf
Answer: B,C
Explanation:
https://docs.splunk.com/Documentation/Splunk/8.1.1/Knowledge/Configureadvancedextractionswithfieldtransforms use transformations with props.conf and transforms.conf to:
- Mask or delete raw data as it is being indexed
-Override sourcetype or host based upon event values
- Route events to specific indexes based on event content
- Prevent unwanted events from being indexed
NEW QUESTION # 78
What are the minimum required settings when creating a network input in Splunk?
- A. Protocol, port number
- B. Protocol, username, port
- C. Protocol, port, location
- D. Protocol, IP, port number
Answer: A
Explanation:
Explanation/Reference: https://docs.splunk.com/Documentation/Splunk/7.3.1/Data/UsetheHTTPEventCollector
NEW QUESTION # 79
......
Splunk Exam Practice Test To Gain Brilliante Result: https://www.test4engine.com/SPLK-1003_exam-latest-braindumps.html
Tested Material Used To SPLK-1003: https://drive.google.com/open?id=1aMPdBYS5T7D1mUIUgfLKDfuWtvlzBSH6